The eight platforms in this portfolio are presented here as case studies in regulatory judgement, not as products. Each one follows the same arc: a compliance failure mode a regulated business actually faces → the control I designed for it → the legal and regulatory reasoning behind that control → the working software that proves the reasoning holds. The law leads; the build is the evidence.
These are specialisms of one person, not separate profiles — the CV sets out the career in outline, and what follows is the detail underneath it.
Honesty first. All eight systems are my own builds and run live in the portfolio, entirely client-side. Private-party data is synthetic throughout, or a dated, frozen dataset in Meridian’s case; the Sanctions Suite carries real, published sanctions and criminal-record data from OpenSanctions under CC BY-NC 4.0 (non-commercial; business use requires a licence); Frontier and Sentinel are decision-support, not legal advice; the applied methods papers are preprints — submitted and pending peer review. Nothing on these pages is a client result, and no confidential or client subject data appears anywhere.
Case study 01 · Financial-crime forensics
FRIS Forensic & Regulatory Intelligence Suite
Sanctions and AML regimes attach to named parties — value hides in third parties. A 23-engine forensic workbench for beneficial-ownership tracing, sanctions & adverse-media screening and deterministic peel-chain analysis, exact to the last unit.
Horizon-scanning tells you a rule changed; the board asks whether it hits us and how hard. A provenance-first intelligence platform where every figure carries its source, timestamp and confidence class — and gaps are shown, never invented.
A forecast you cannot defend is a risk, not a plan. A dependency-free forecasting engine that shows its error before its forecast — models chosen by back-tested performance on rolling origins, never by fashion.
Regulatory programmes miss statutory dates on sequencing and capacity, not intent. A scheduling engine that turns a written brief into a live programme — log a delay and every view re-plans, keeping the record of why.
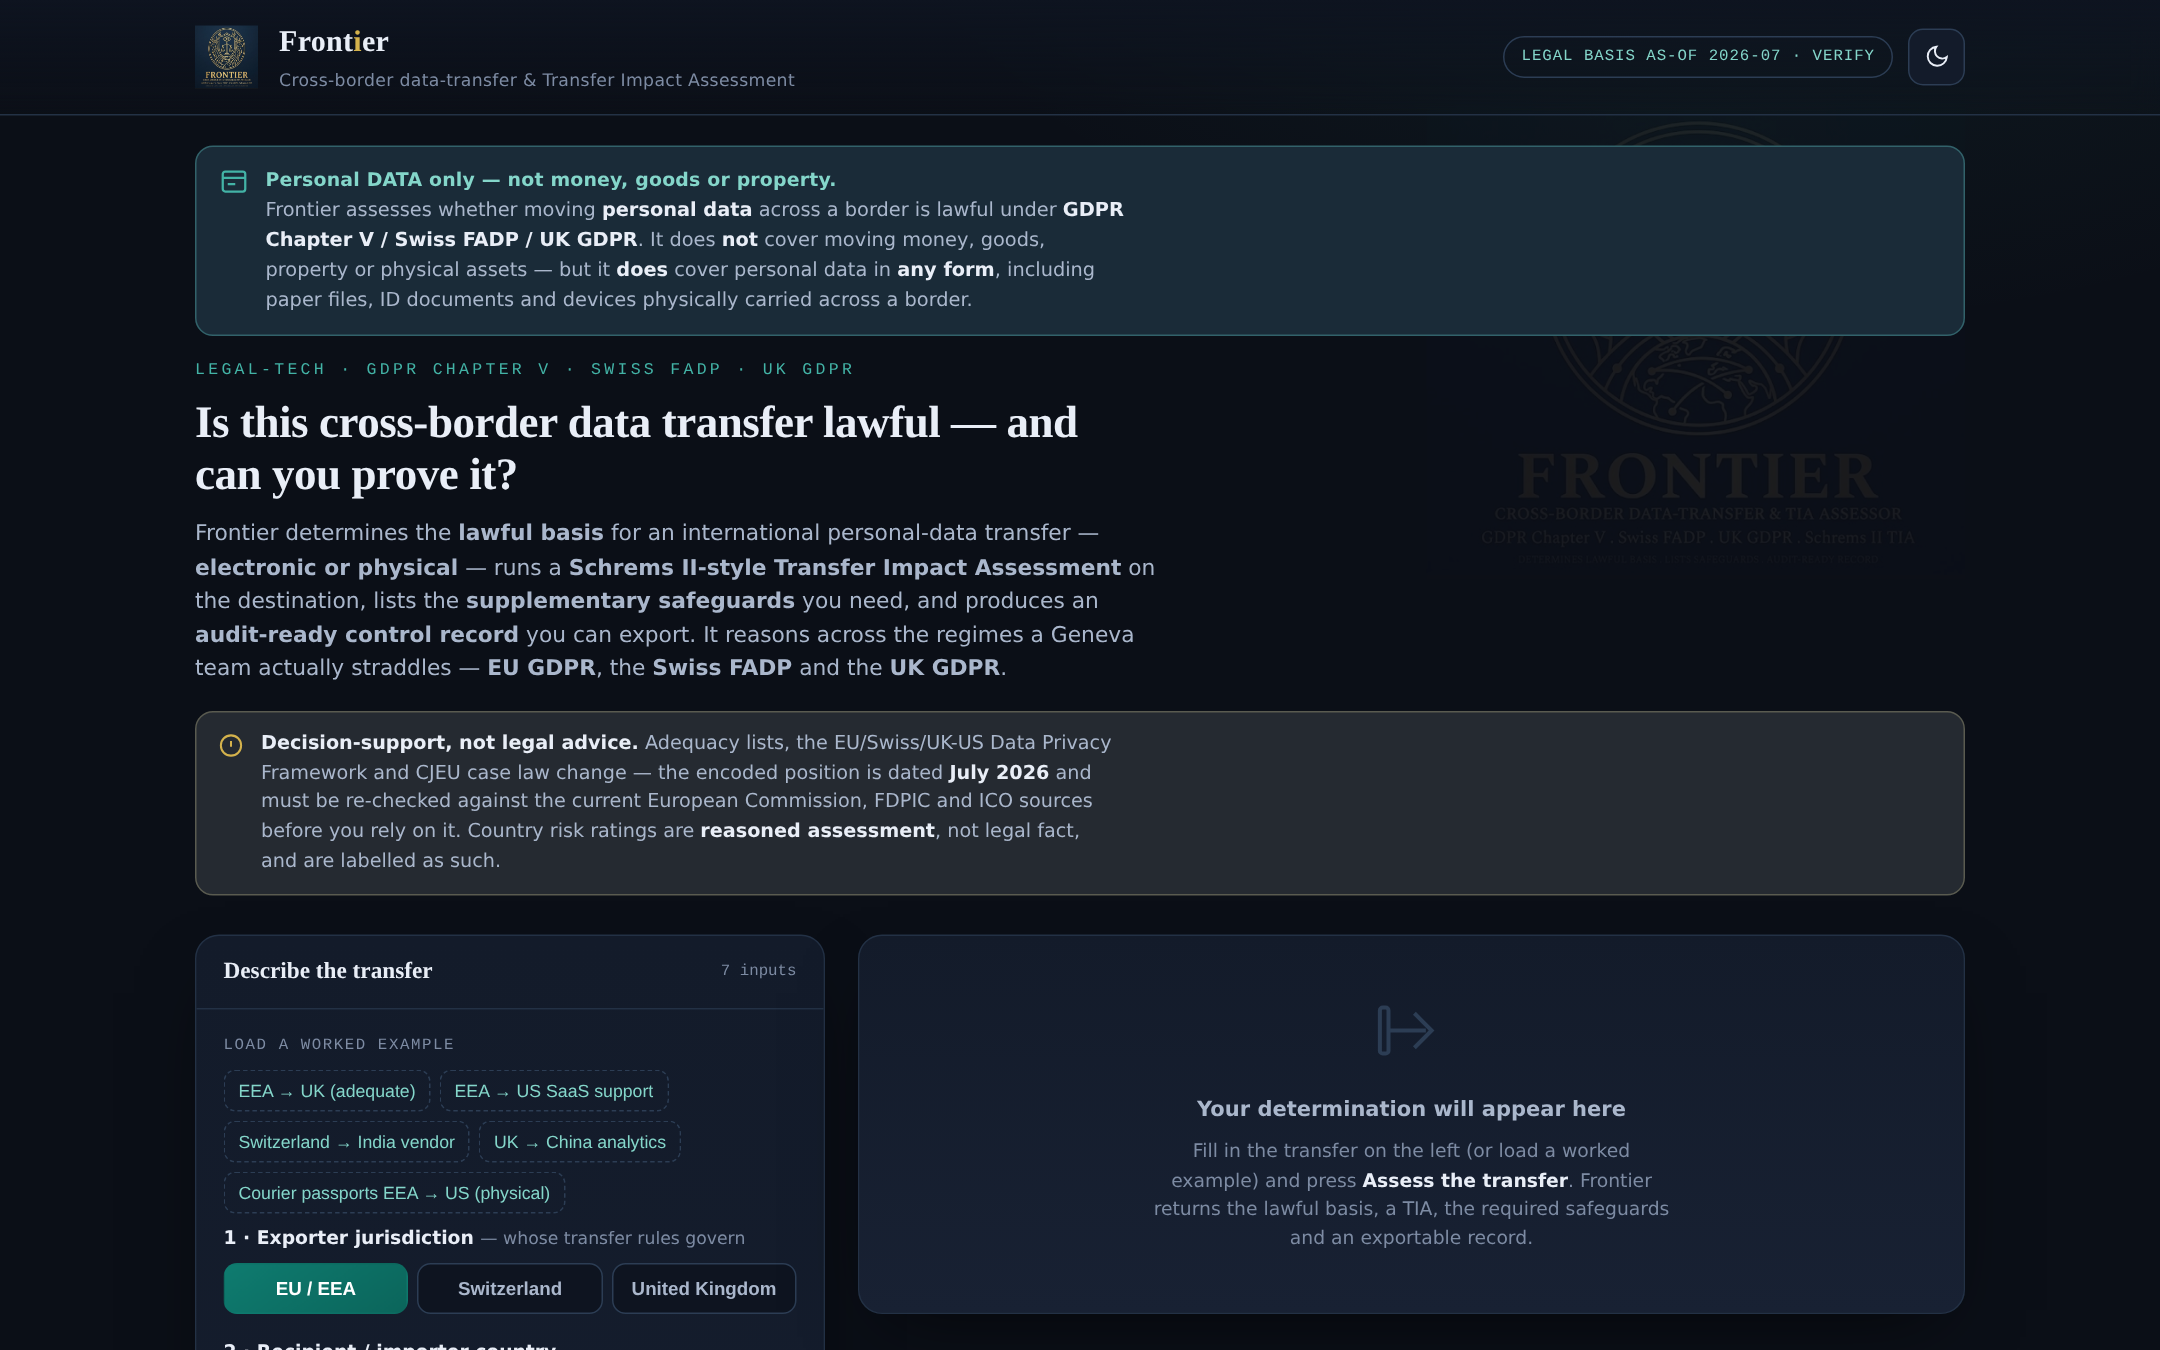
Is this cross-border transfer lawful — and can you prove it? Three regimes in one rules engine (EU GDPR Chapter V, Swiss FADP, UK GDPR), a Schrems II-style transfer impact assessment, and an audit-ready exportable record.
GDPR Ch. V · FADP · UKSchrems II TIAAdequacy · SCCs · derogations
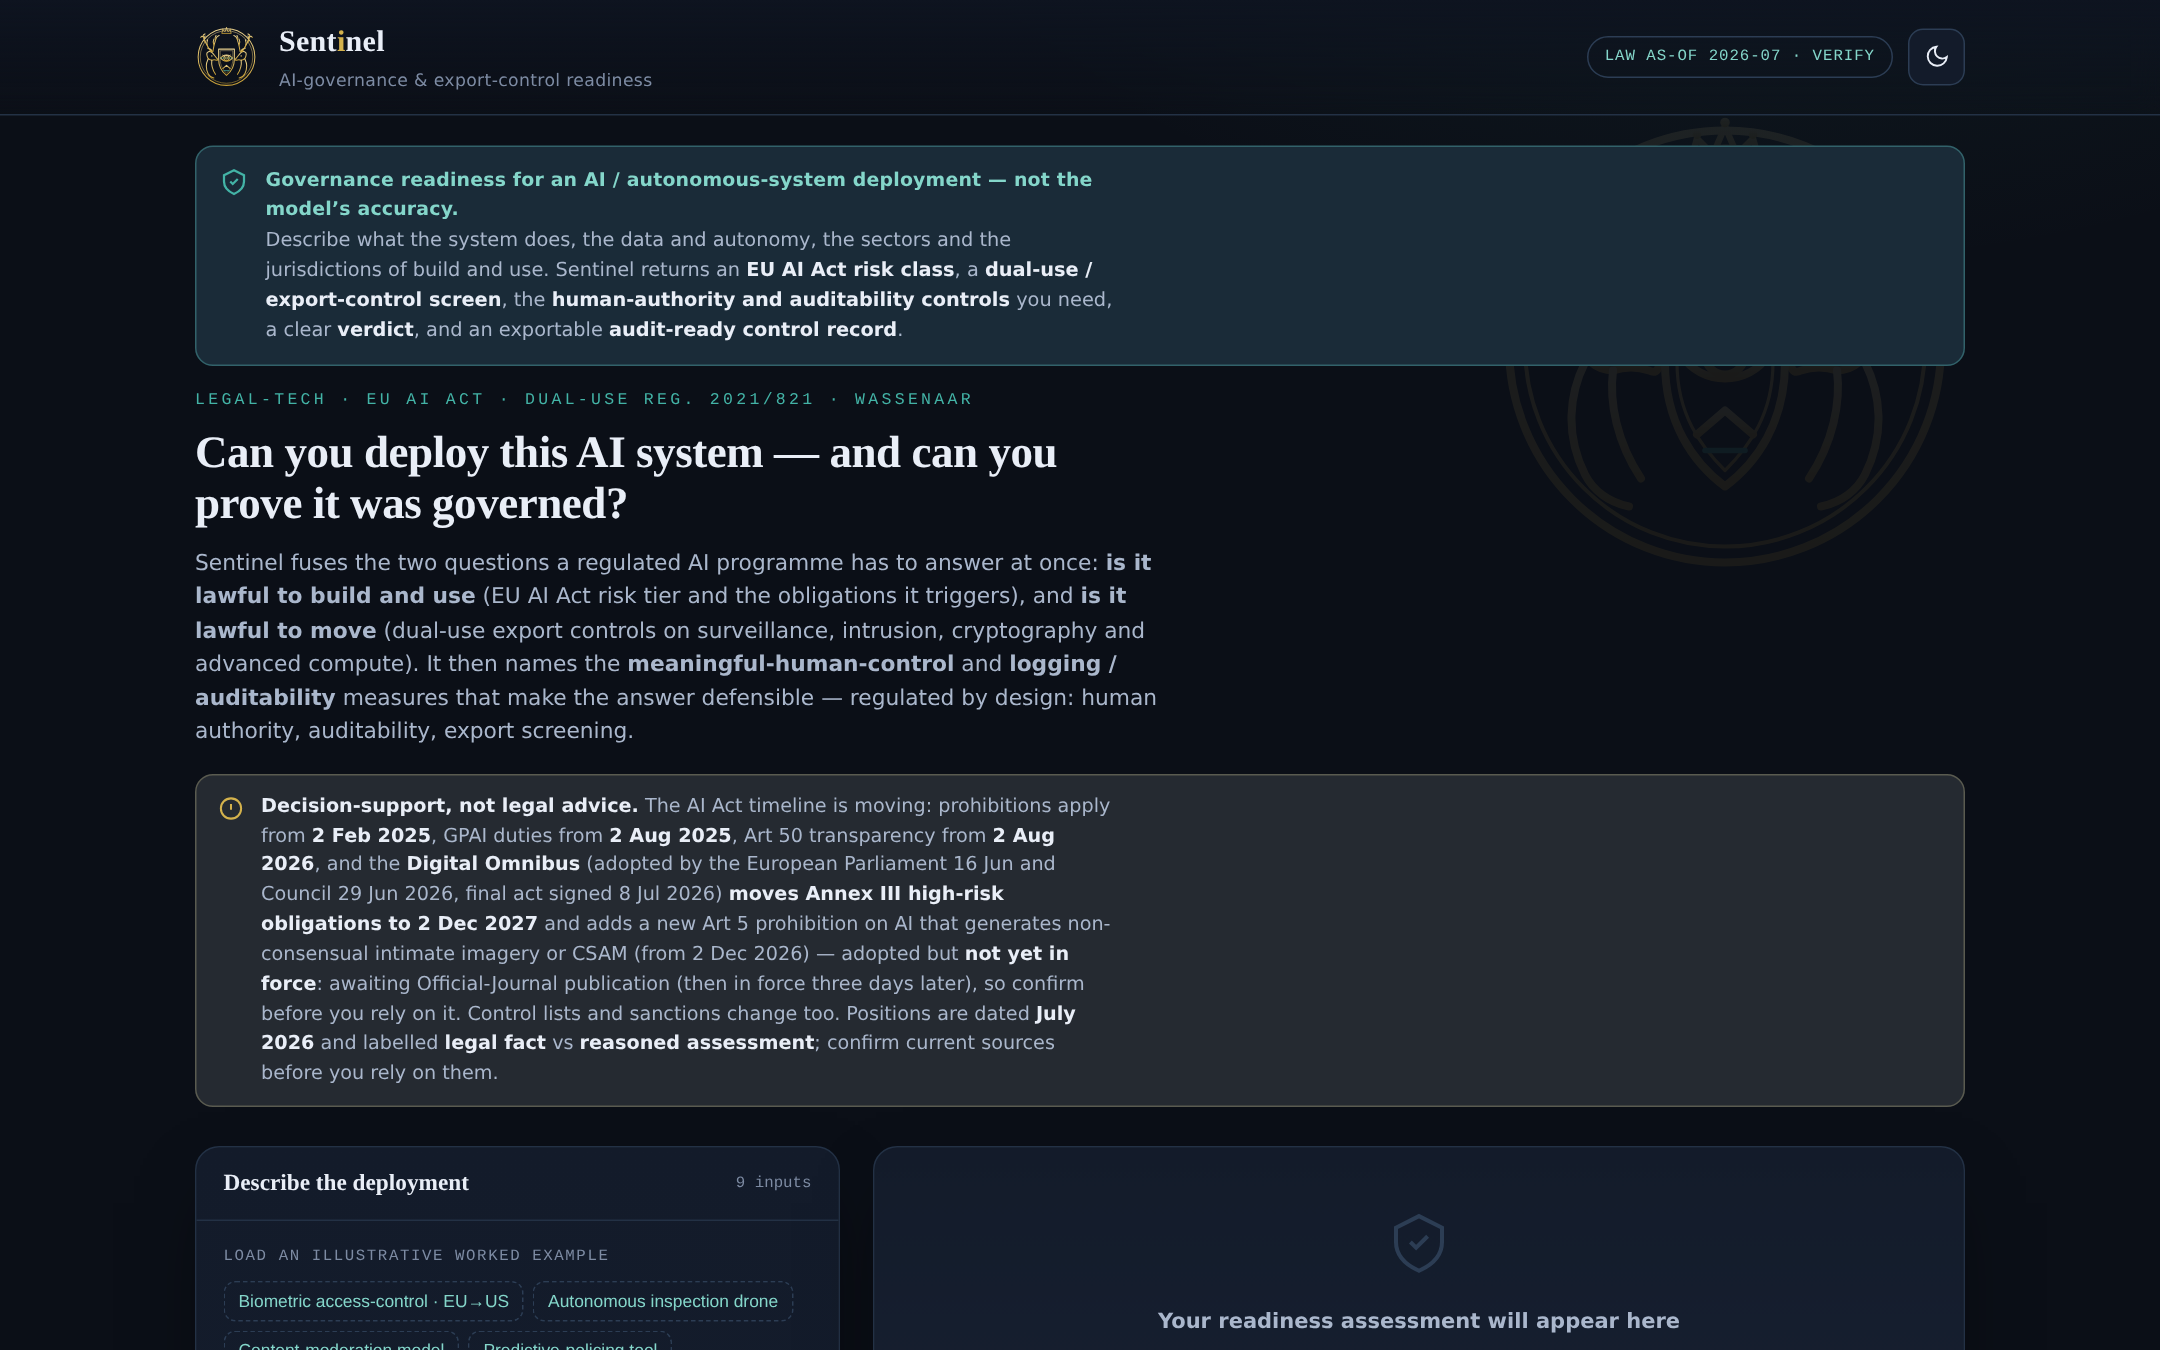
Two bodies of law, almost never assessed together: lawful to build and use (EU AI Act) and lawful to move (dual-use export controls). Sentinel answers both in one deterministic pass, with an audit-ready control record.
EU AI Act · Annex IIIDual-use 2021/821Wassenaar Cat 3/4/5Human control · logging
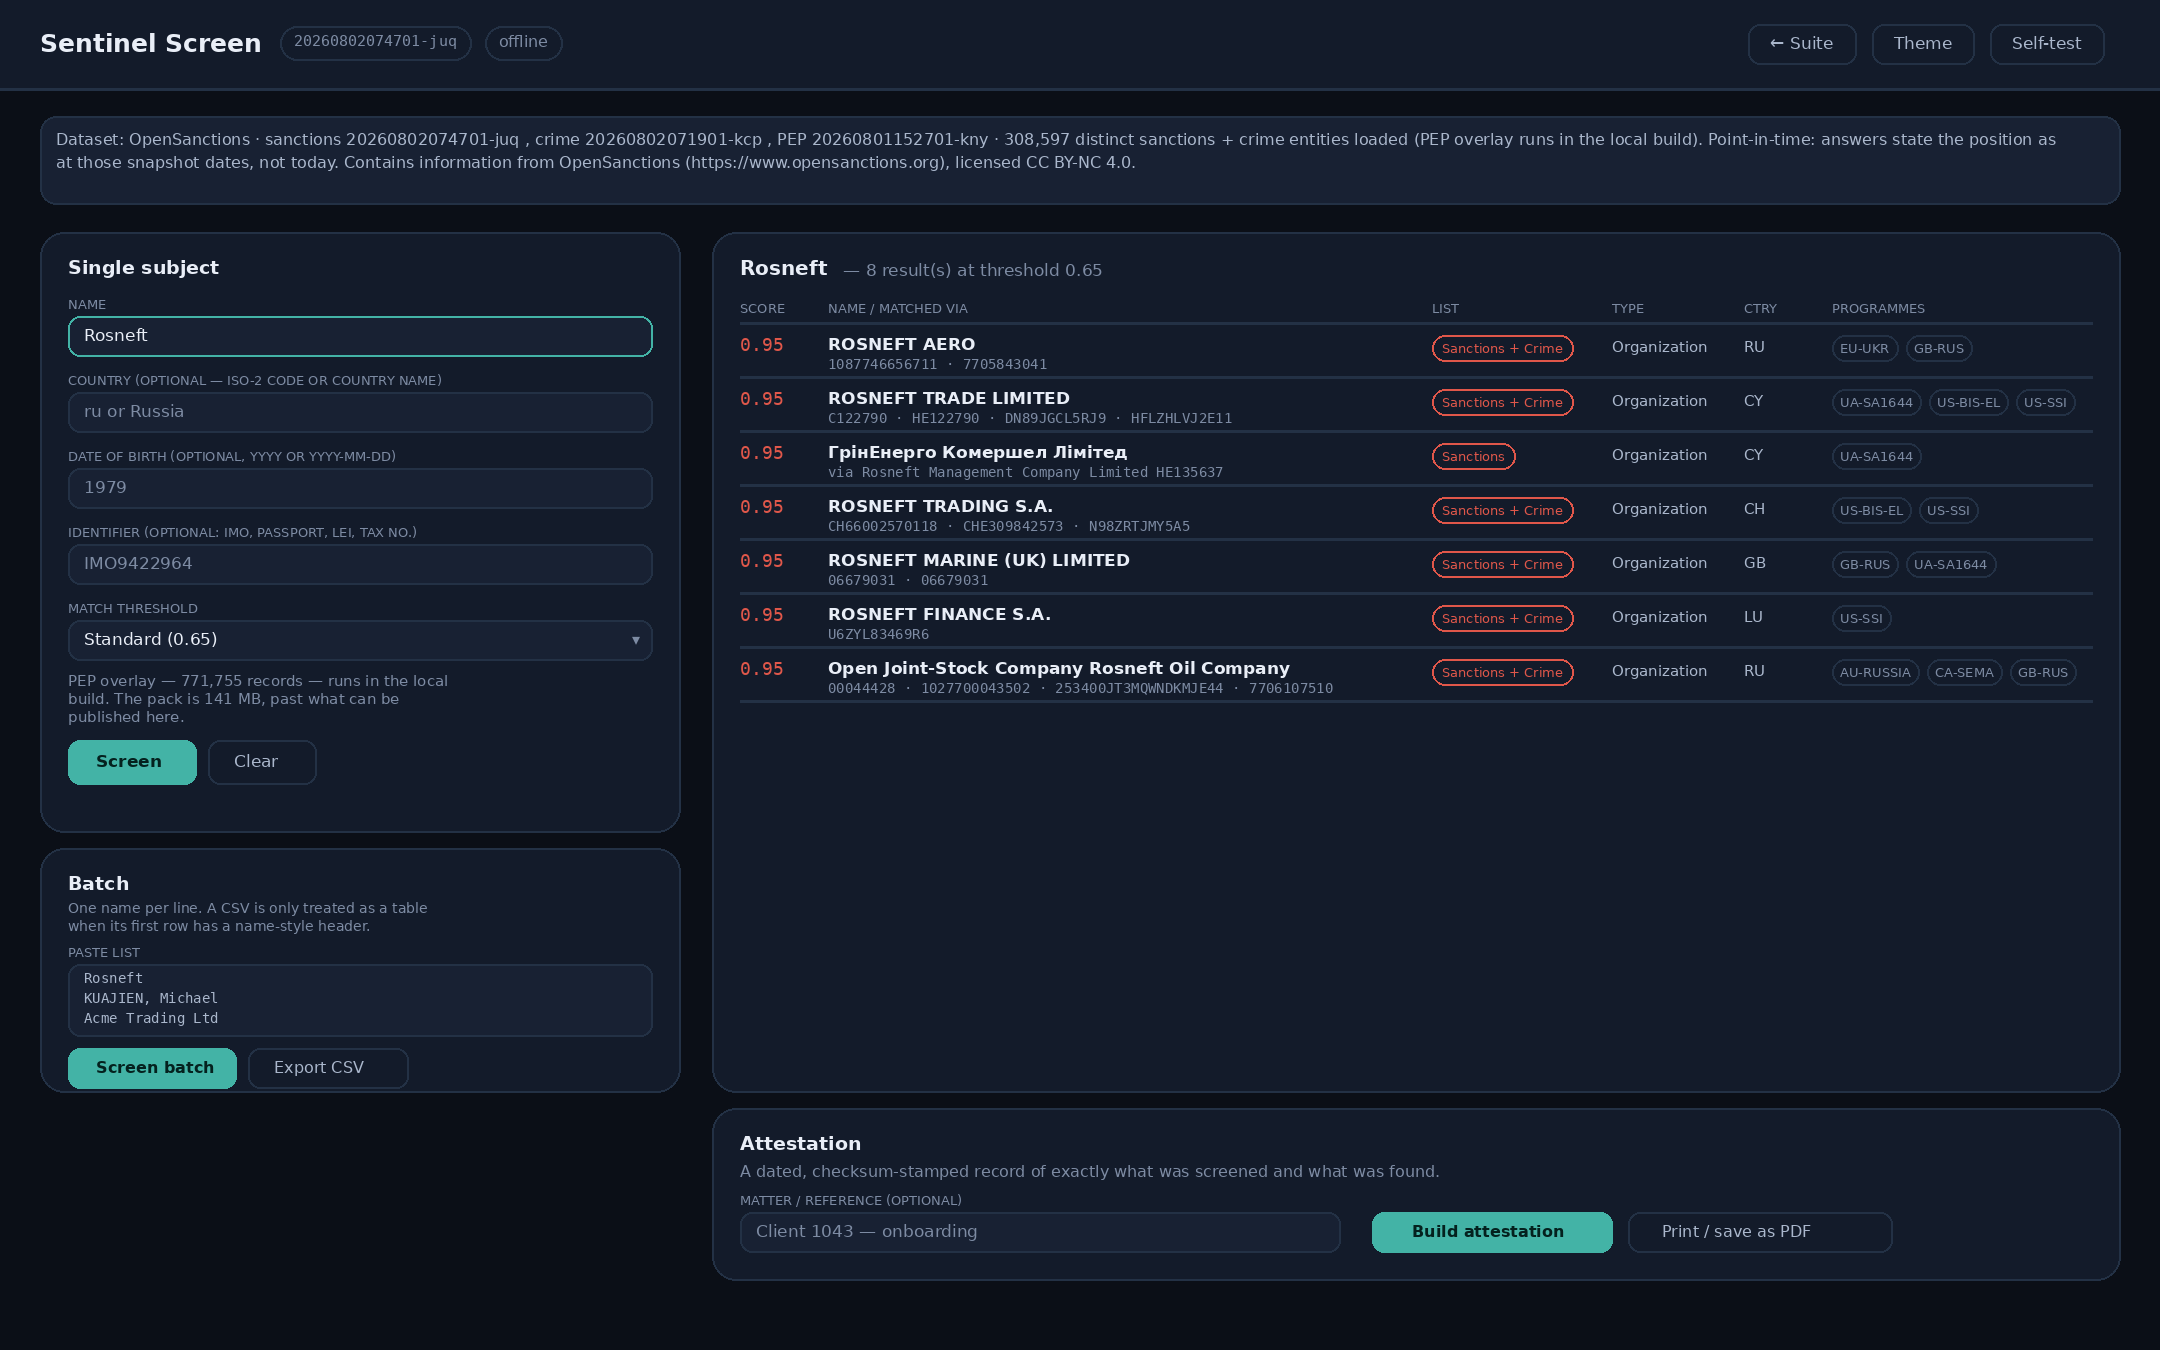
Sanctions Suite Screening, exposure, vessels, portfolio
Screening bought as a subscription stops the moment the subscription does — and still leaves three things unsaid: as at when, on what corpus, and why this record. Four offline tools on one dated, checksummed snapshot that answer all three, and produce an attestation you can put in the file.
Three instruments that check a claim against the authoritative register with the network disconnected: where an economy’s supply is concentrated and whether anyone could replace it; whether a cited authority exists and is what the citation says; who consolidates whom. Each states what it cannot see as plainly as what it can.
323,929 trade cells479,762 control relationships65,357 retractionsAir-gapped