CF
Christopher Farmer
Geneva · Swiss B permit — work-authorised, no sponsorship needed · available now

I turn strategy into operating reality — programmes delivered, operating models redesigned, and the systems that make the change stick.

A strategic operator and legally trained consultant. Nearly a decade leading an eight-site organisation, ultimately with full executive authority: I identify the decisive constraint, align executives and specialists, and convert analysis into decisions, control architecture, working systems and measurable delivery.

Strongest where transformation meets regulation — legal operations, business continuity and organisational resilience, AI governance — and unusually hands-on with the technology: the eight platforms on this site are mine, engines and interfaces included, so the plan, the controls and the tooling come from one pair of hands.

LinkedIn
Where I fit

The roles I am aiming for, and the evidence behind each

Four lanes, one CV. Open a lane for the titles it covers, how I work in it, and where the proof sits on this site.

01

Strategy execution & transformation

Operating models designed and run, not just drawn.

  • Moved an eight-site organisation from paper to cloud in under three months during COVID — continuity preserved at every site, operating costs permanently cut by about 30%.
  • Designed the split operating model that materially reduced a developer-led business's capital burn, and helped shape emergency-directory and ambulance-dispatch systems for Philippine island communities.
  • Built Helm, a scheduler that reads a brief, plans, staffs and re-plans around blockers, and Vantage, a forecasting engine that shows its error before its forecast.
02

Programme, portfolio & PMO leadership

Governance that works in practice — gates, registers, evidence and escalation.

  • Converted government, statutory and funder obligations into approval gates, risk registers, escalation routes, evidence logs and accountable workflows — an unblemished audit and inspection record, with audit retrieval in under 15 minutes.
  • Won a £200,000 ESF and National Lottery partnership, contributed to more than £500,000 in successful public and lottery bids, and governed restricted funding against demanding evidence and reporting conditions — under 1% funding exceptions.
  • Applied my scheduling engine inside Morris Anderson Construction's client and admin portals and cost estimator — a business delivering multi-million-pound building projects.
03

Legal operations, regulatory change, risk & controls

The legal, commercial and people-risk backbone, owned end to end.

  • Six years owning legal, compliance and operations: supplier, partner and funding agreements; GDPR, safeguarding and policy architecture; disputes, grievances, capability processes and restructuring, all with defensible records.
  • As a trustee, steered a sensitive employment dispute to early, documented resolution — averting more than £70,000 in tribunal exposure — and supported the board through consecutive deficit years.
  • Built the tooling a legal-operations team would otherwise buy: FRIS (financial-crime forensics, 23 engines), the Sanctions Suite, Frontier (cross-border data transfer and TIAs) and Meridian (regulatory-impact tracking) across UK, EU and Swiss regimes.
04

AI enablement & technology governance

Agentic AI and deterministic decision systems — adopted with controls, not hype.

  • Advanced practical fluency in agentic workflow architecture: retrieval and decision logic, tool constraints, source provenance, evaluation, audit trails and human review — the parts that make an AI system defensible in a regulated business.
  • Built Sentinel, an EU AI Act and export-control readiness assessor, and apply the same discipline to every platform here: dated, evidence-tagged, exportable outputs that never purport to replace the decision-maker.
  • Led technology adoption for real — paper to cloud across eight sites with the training, policies and controls that made it stick — with working Python, SQL and REST/JSON, and advanced Excel, Power BI, Jira and Confluence.

civfarmer@gmail.com · linkedin.com/in/civfarmer · Geneva · Swiss B permit — work-authorised

100% audit
Inspection pass — board, funders & regulators
8-site org
Legal, compliance & operations owned end-to-end
£200k secured
+ £500k+ competitive bids authored — ESF, Lottery & government
8 platforms
Working legal-tech & analytics systems built
−30% operating cost — paper-to-cloud in under 3 months
£70k+ tribunal exposure mitigated — early settlement strategy
<15 min audit retrieval · <1% funding exceptions
$2M+ solar JV — white paper, deck & financing
Portfolio — live regulatory tooling

Eight platforms I designed and built

For a RegTech or legal-engineering team, this is the part of the portfolio that carries the weight: working tools where I own both the regulatory reasoning and the code that runs it — FRIS, the Sanctions Suite, Ground Truth, Frontier and Sentinel are the compliance-tech proof; Meridian, Vantage and Helm extend the range. Each opens right here in the page — click a card to launch it, read a short “How it’s built” note, or pop it out to a new tab.

Architected and built by me: the analysis engines, data models and interfaces are mine. All eight run client-side — everything (including a locally-vendored React where it is used) computes entirely in your browser, so no subject data ever leaves the page. All data is synthetic or a dated, frozen local dataset.

Flagship · Forensic intelligence▶ Live demo FRIS home workspace — dark navy forensic UI with module sidebar and Synthetic Demo Data label

FRIS Forensic & Regulatory Intelligence Suite

A forensic workbench for financial-crime investigations — 23 analysis engines spanning beneficial-ownership tracing, sanctions & adverse-media screening, crypto peel-chain tracing and an insolvency-recovery waterfall. A single-author codebase of ~20,000 lines of JavaScript.

23 engines · ~20k LOCVanilla JSGraph engineOffline
New tab Case study Synthetic data
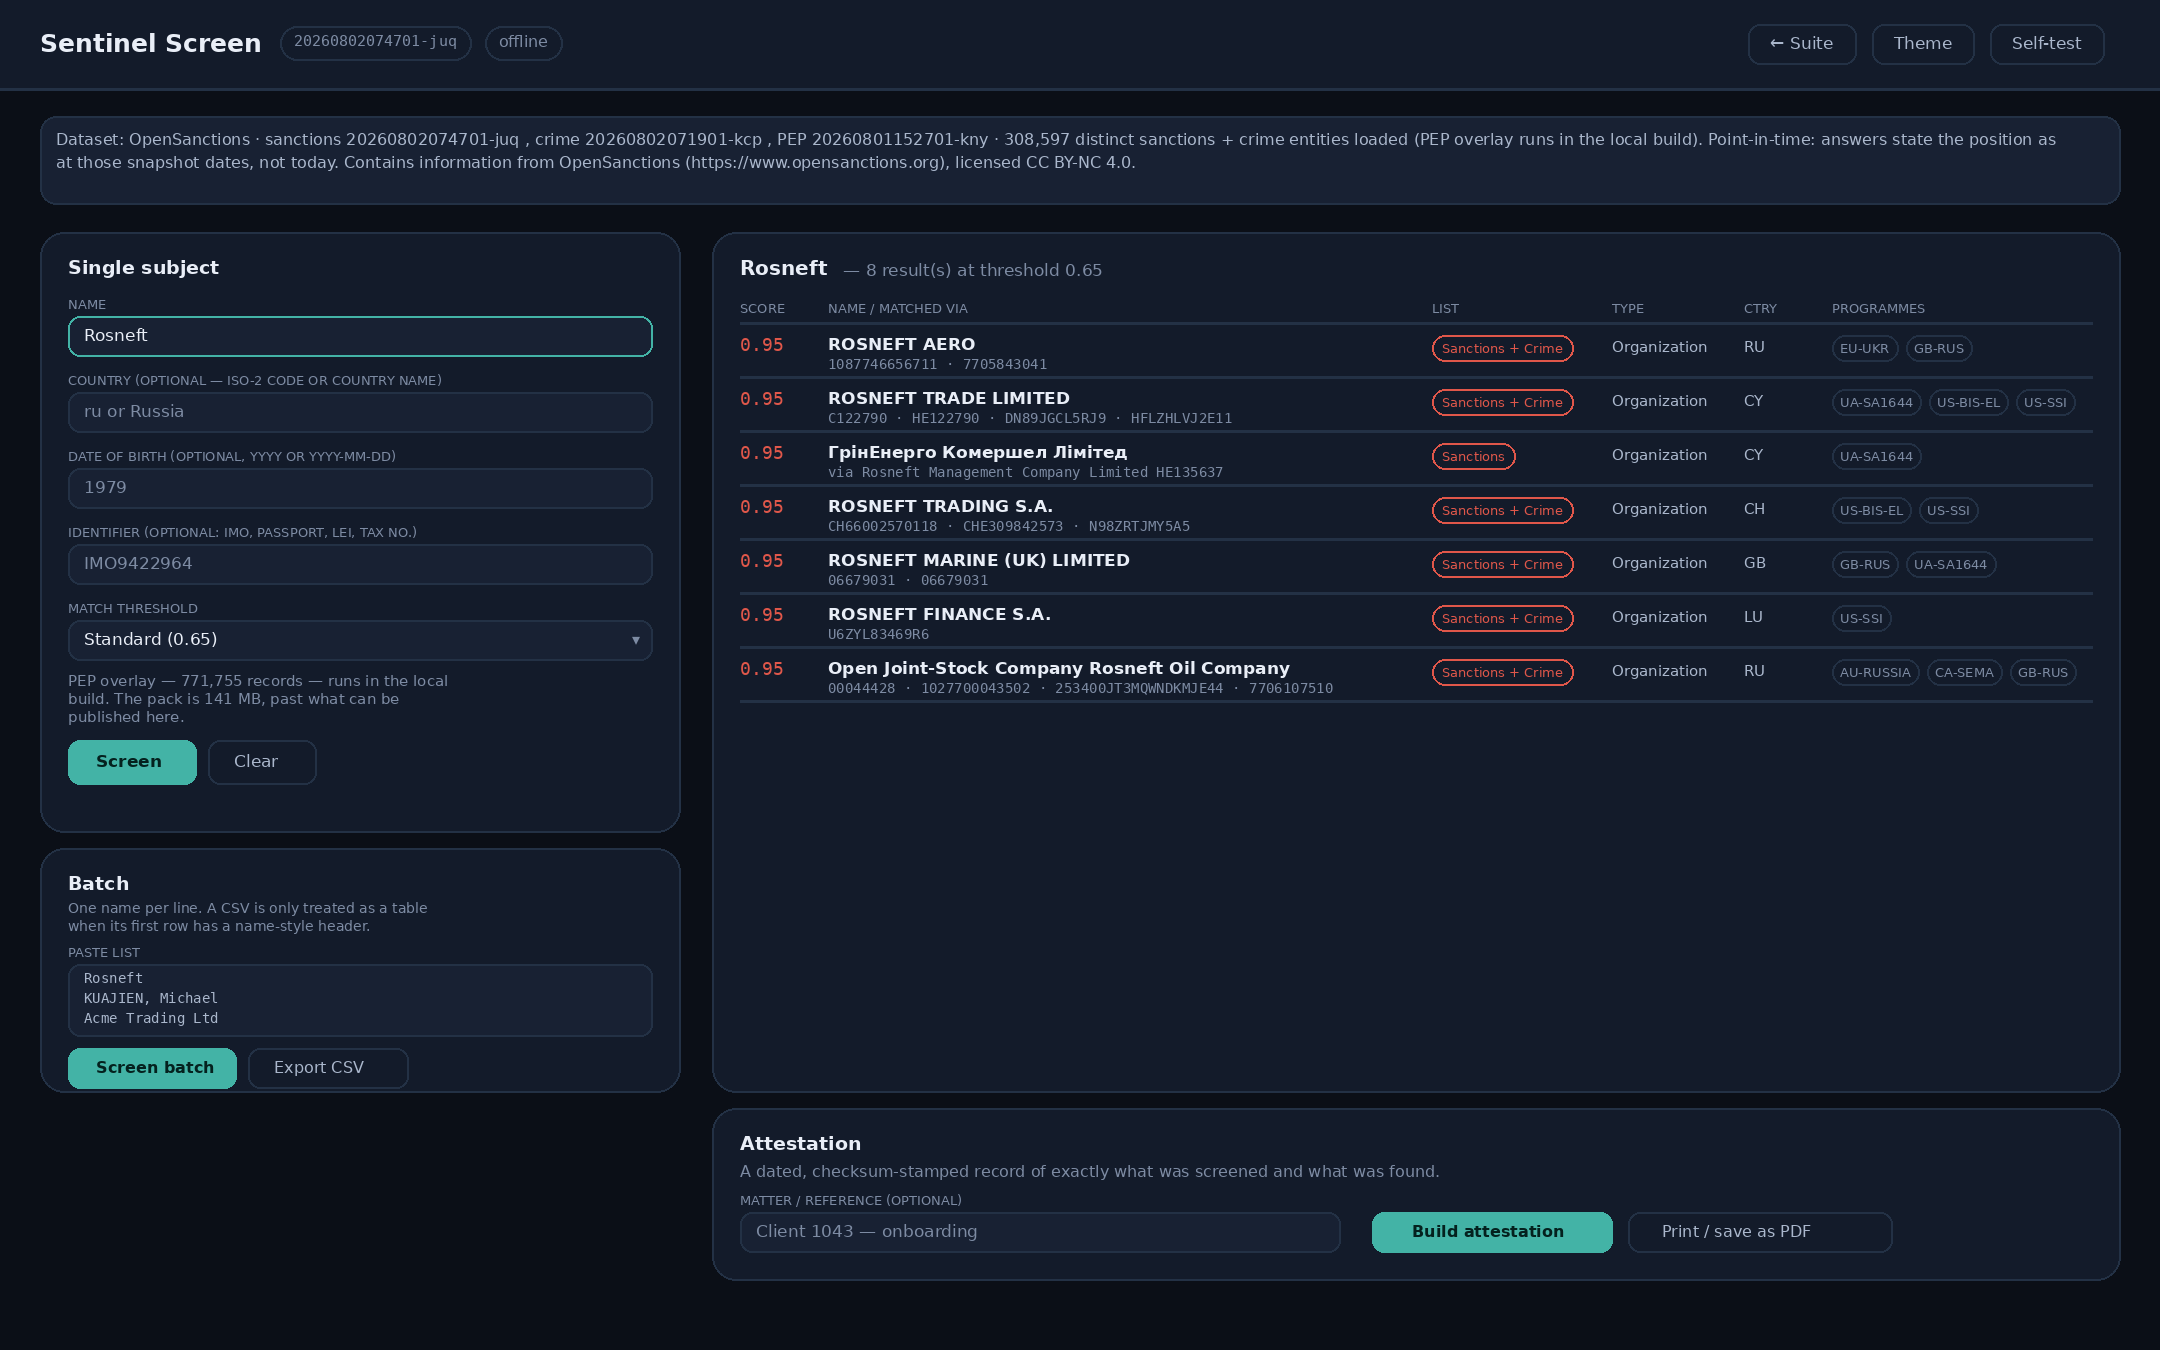
Sanctions screening & exposure▶ Live demo Sentinel Screen returning eight sanctioned Rosneft entities with scores, list labels and sanctions programmes

Sanctions Suite Screening, exposure, vessels, portfolio

Four tools on one dated, checksummed OpenSanctions snapshot — 308,597 sanctions and crime entities (73,026 of them sanctions-listed), 12,113 ownership and association records, 2,347 vessels and aircraft. Screen a name or a manifest, trace a counterparty's route to a designated party, and produce a dated attestation with source checksums. No API, no subscription, no data leaving the page — so it still works where the network is unavailable, untrusted, or where the query itself is the sensitive part.

Python pipelineVanilla JSDeterministic matchingOffline
New tab Case study Runs air-gapped · OpenSanctions, CC BY-NC 4.0
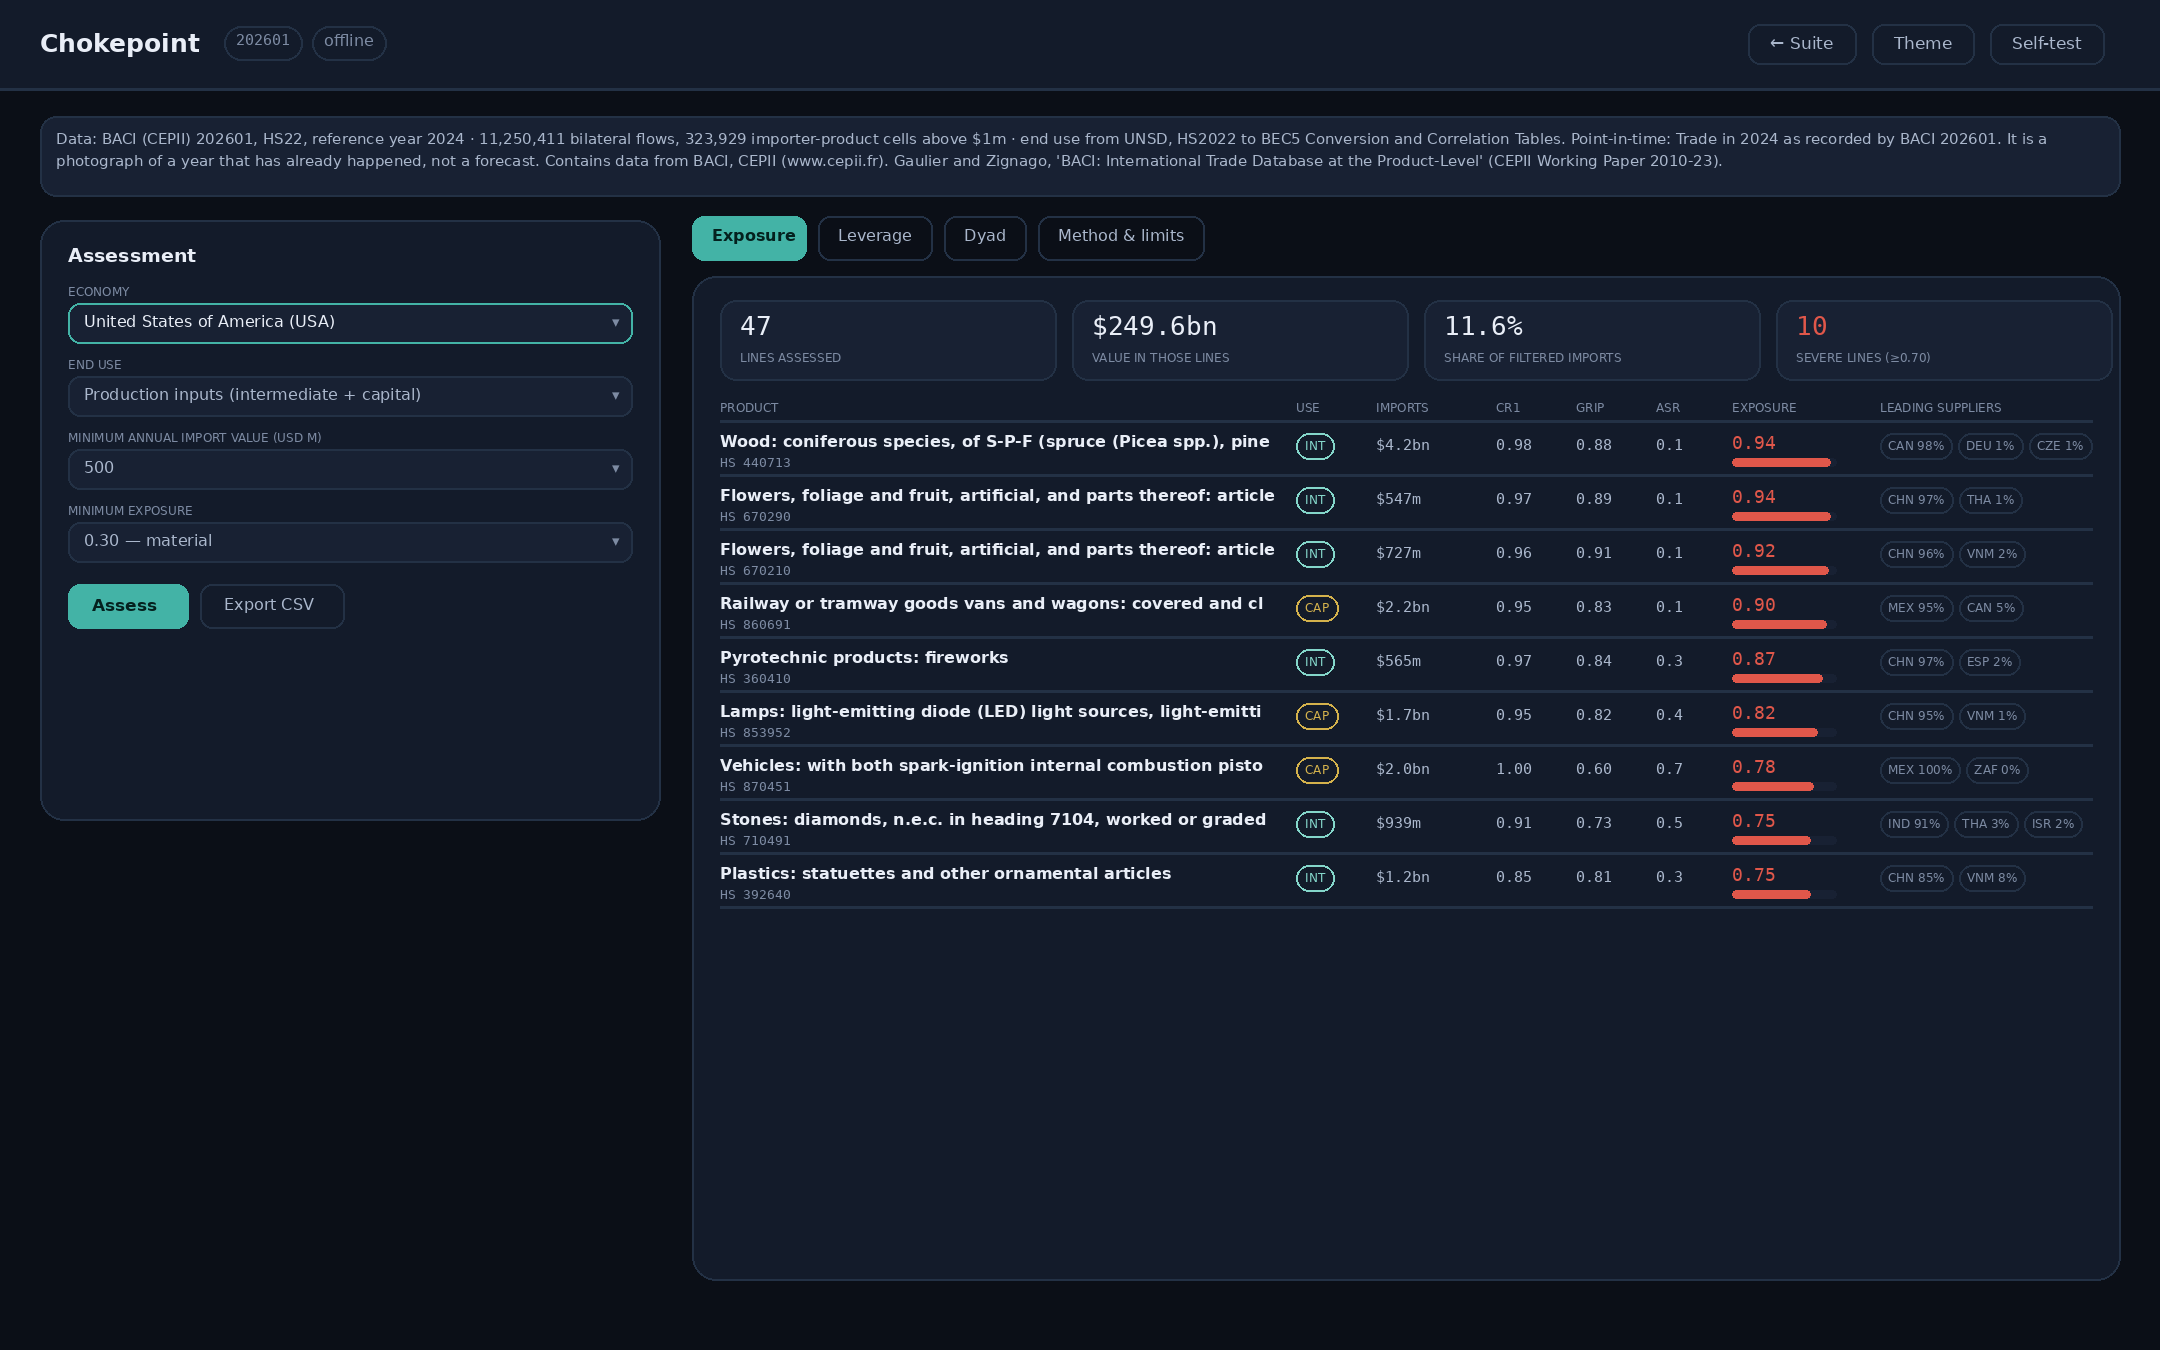
Verification & economic security▶ Live demo Chokepoint ranking the United States’ most concentrated production inputs, with supplier shares, world grip and exposure scores

Ground Truth Chokepoint, Veritas, Lineage

Three instruments that check a claim against the authoritative record with the network disconnected. Chokepoint scores economic coercion exposure across 323,929 importer-product cells of 2024 trade. Veritas tests whether a cited authority exists, resolves to the case it is attributed to, and has not been retracted. Lineage walks 479,762 filed corporate control relationships. Each states what it cannot see as plainly as what it can.

Python pipelineVanilla JSBACI · GLEIF · Find Case LawAir-gapped
New tab Case study Runs air-gapped · dated open-data snapshots
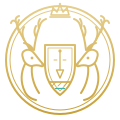
Regulatory & market intelligence▶ Live demo Meridian companies view — coverage-gated issuer list with provenance labels and coverage warnings

Meridian Regulatory-impact market tracker

A market tracker that flags the regulatory changes most likely to hit a company — matching new rules, amendments and sanctions moves to each issuer's actual business and pipelines, then showing whether the exposure could move the share price, and why. Provenance-first: every figure carries its own source and as-of date, and gaps are shown, never invented.

PythonSQLiteProvenance modelFrozen dataset
New tab Case study Full platform · frozen dataset
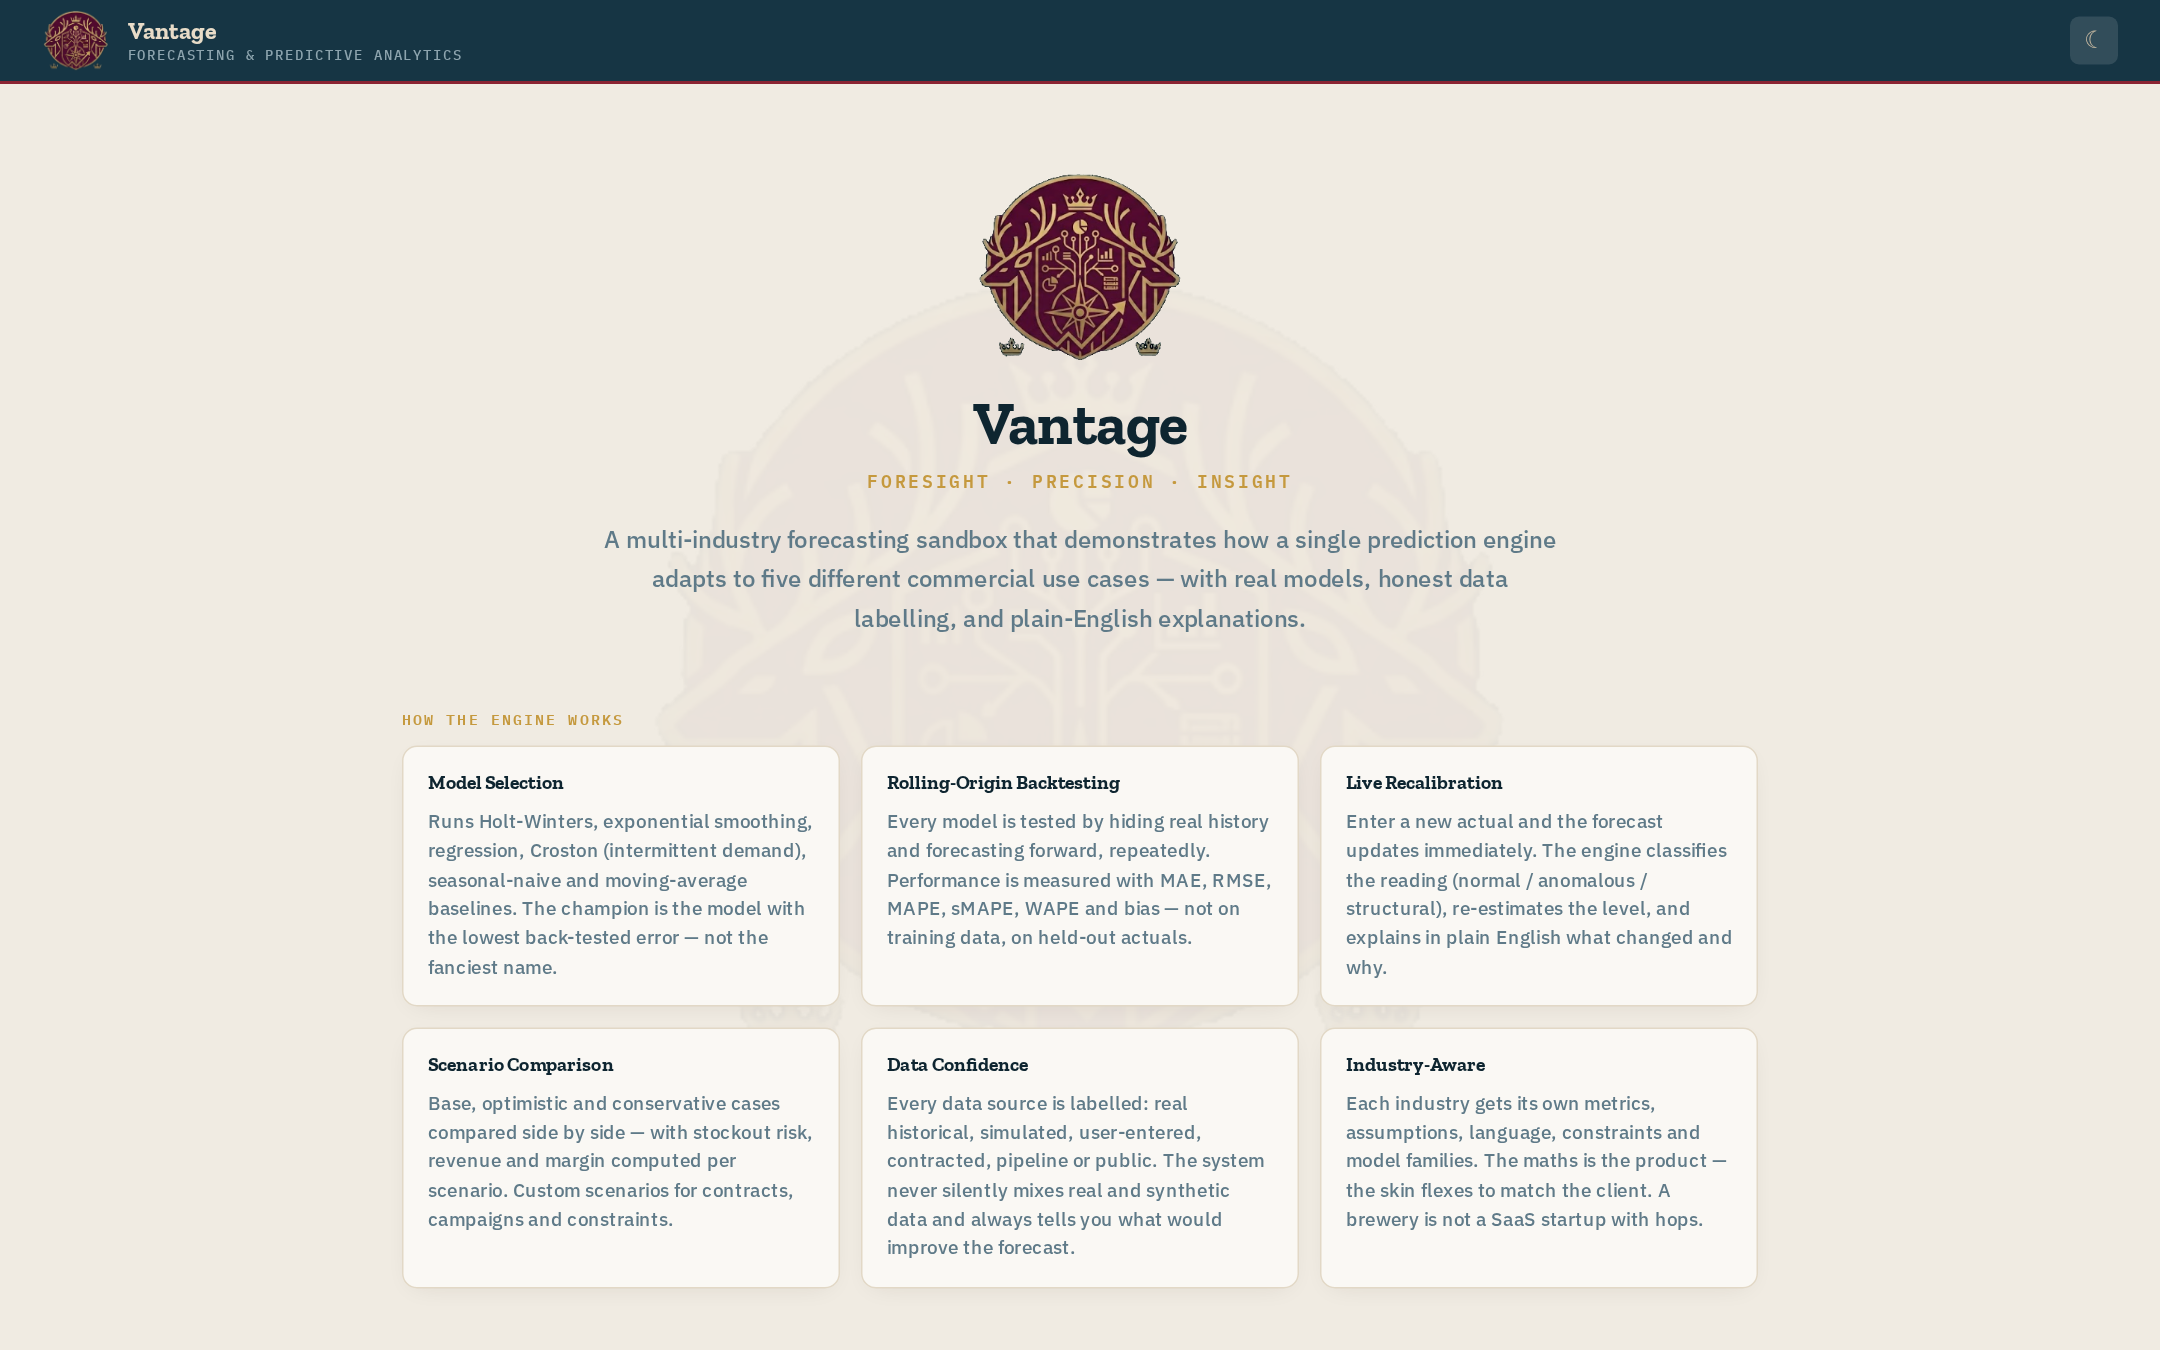
Forecasting & analytics▶ Live demo Vantage landing view — crest, strapline and six engine-capability cards

Vantage Predictive analytics sandbox

A multi-industry demand-forecasting sandbox — brewery, DTC, education, manufacturing and SaaS — with a dependency-free engine (Holt-Winters, ETS, Croston, OLS) back-tested on rolling origins and planned over operationally sensible weekly or monthly horizons. Load a worked scenario or bring your own numbers.

Forecasting engineHolt-Winters · ETSBack-testing
New tab Case study Live app · runs offline · synthetic data
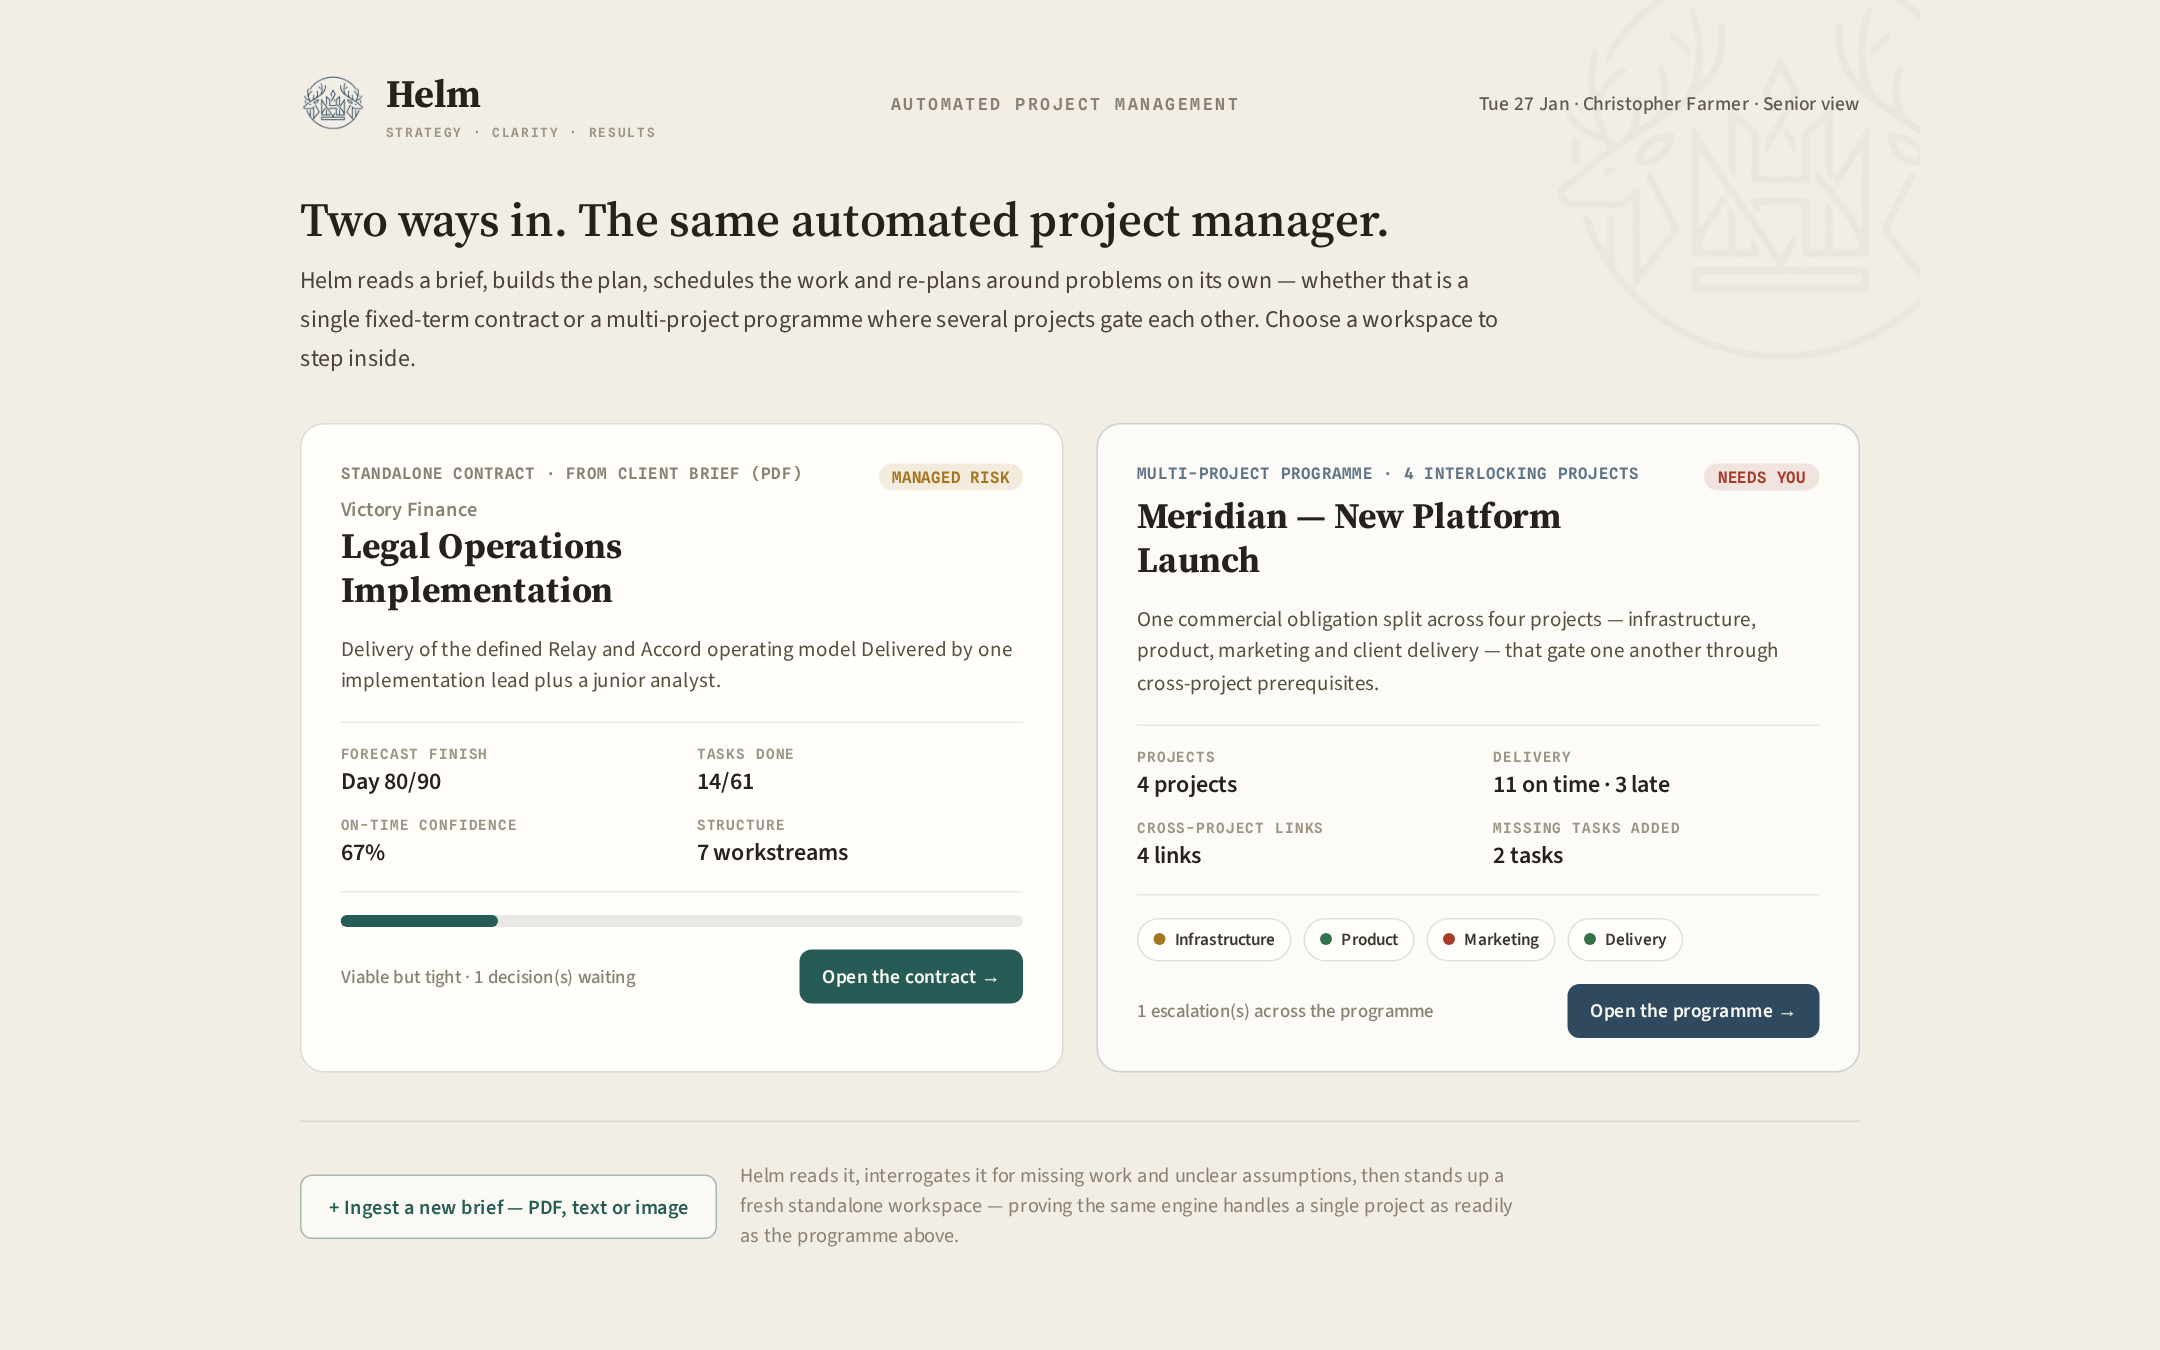
Automated project management▶ Live demo Helm senior view — two workspace cards with forecast finish, confidence and programme status

Helm Automated PM platform

A project-management platform that turns a written brief into a live schedule — dependency graphs, capacity and critical-path planning, editable tasks you can split, reorder and re-scope, blocker tracking, and a multi-project portfolio view. Log a delay and every view re-plans around it.

Scheduling engineDependency graphBrief parser
New tab Case study Live app · runs offline · synthetic data
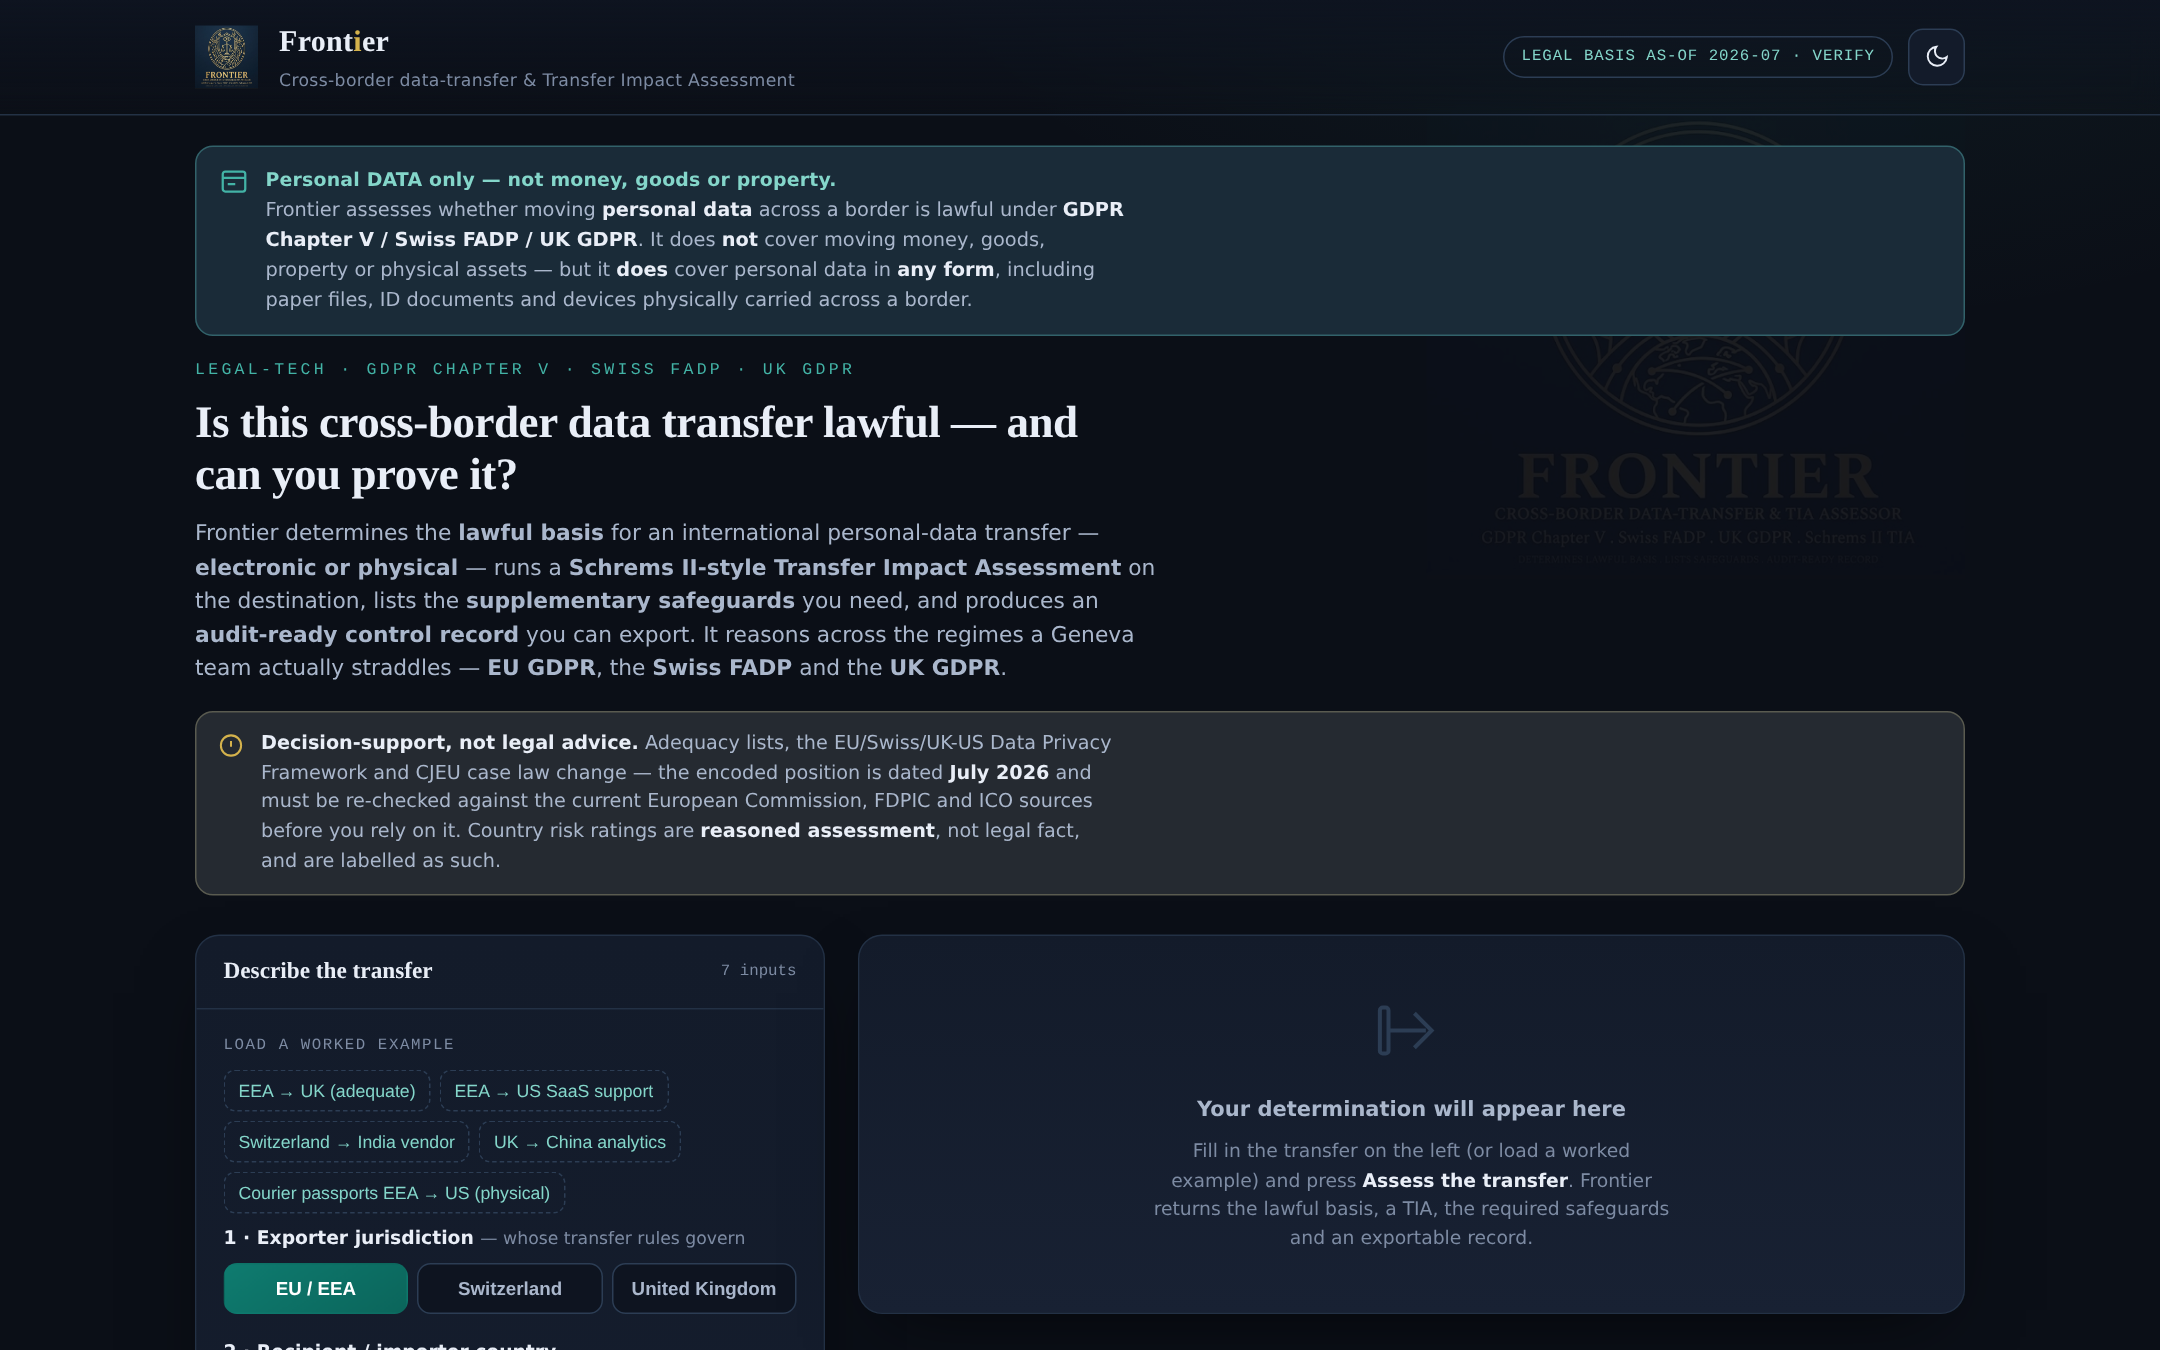
Legal-tech · Data-transfer & TIA▶ Live demo Frontier workbench — transfer form with worked examples and dated legal-basis banner

Frontier Cross-border data-transfer & TIA

Determines the lawful basis for moving personal data across a border — EU GDPR Chapter V, the Swiss FADP and UK GDPR — runs a Schrems II-style Transfer Impact Assessment on the destination, lists the supplementary safeguards you need, and exports an audit-ready record. Handles electronic and physical transfers alike; positions are labelled legal-fact vs assessment and dated, with a “verify current lists” caveat.

GDPR Ch. V · FADP · UKSchrems II TIAAdequacy · SCCs · derogationsOffline
New tab Case study Offline · decision-support, not legal advice
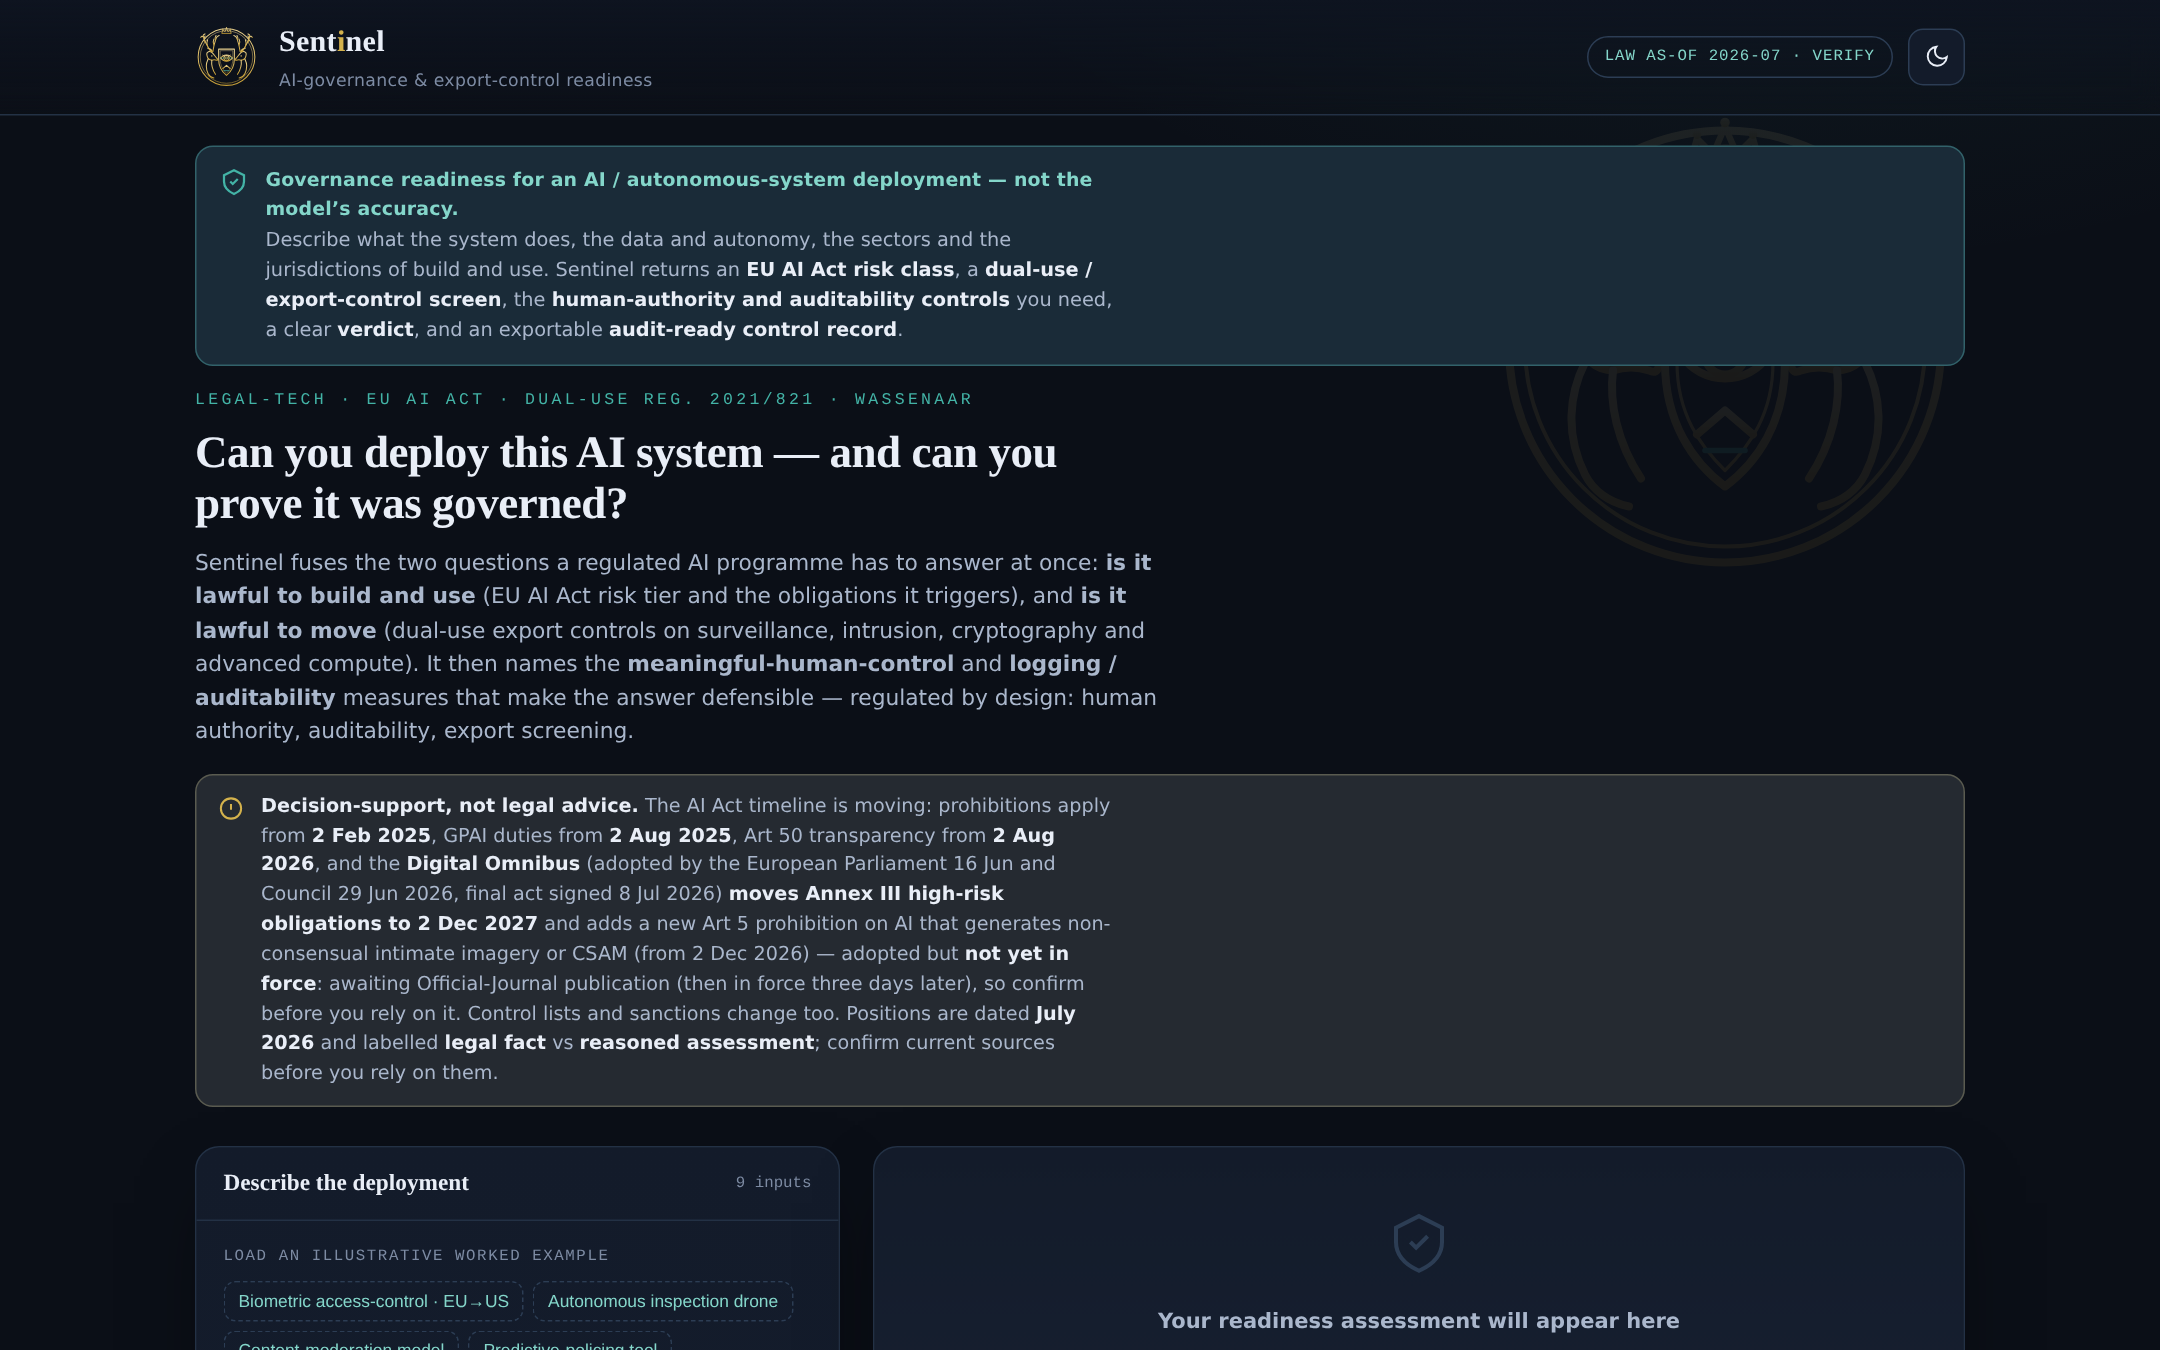
Legal-tech · AI governance & export control▶ Live demo Sentinel workbench — deployment form and dated AI Act timeline advisory

Sentinel AI-governance & export-control readiness

Describe an AI / autonomous-system deployment; Sentinel returns its EU AI Act risk class (prohibited / high-risk / limited / minimal) with the obligations triggered, a dual-use export screen — EU Reg. 2021/821 cyber-surveillance catch-all, Wassenaar Cat 3/4/5, with an honest US ITAR/EAR flag — the meaningful-human-control and auditability controls needed, a clear verdict, and an audit-ready control record. Positions are dated and labelled legal-fact vs assessment.

EU AI Act · Annex IIIDual-use 2021/821 · WassenaarHuman control · loggingOffline
New tab Case study Offline · decision-support, not legal advice
Client work — commercial build
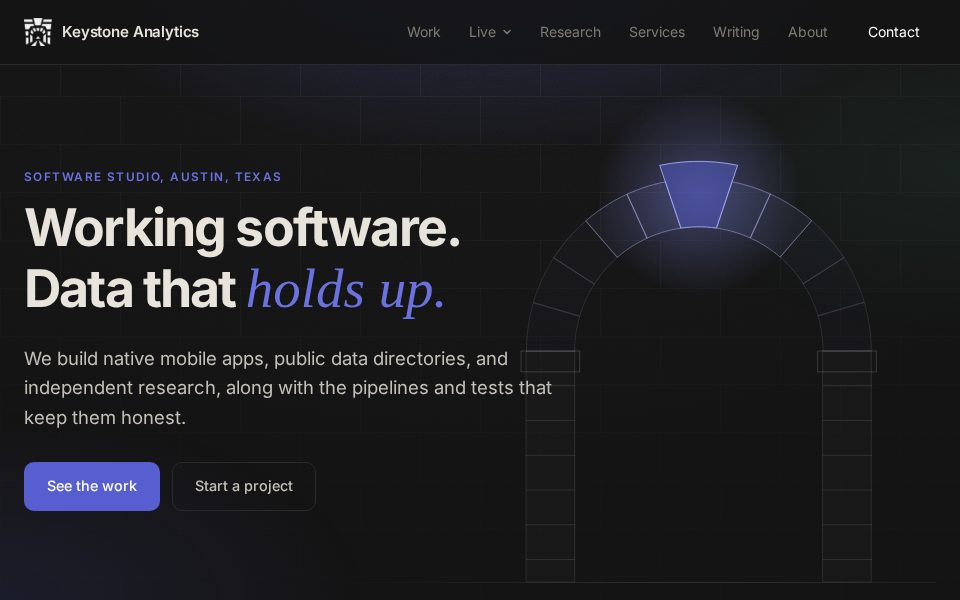
Consultancy client▶ Preview Keystone Analytics — the studio's home page

Keystone Analytics Consultant · legal, compliance & technology

A software studio that ships native apps, public-data directories and research audits. I advise on legal, compliance, financial and strategic matters across its applications and ventures and help shape the data and risk logic behind them — including the compliance and rollout framework for AidNow, its verified emergency-services directory for Negros Island. The Work page is the shipped record.

Advisory · compliance frameworksAI / LLM workflow governanceProduct & data logic
Visit the site Their work Their site, their numbers — the advisory role is described in Experience
Commercial client build▶ Preview Morris Anderson Construction mark — gold monogram on the dark client-build palette

Morris Anderson Construction Website · estimator · client portal

A production system built end-to-end for a UK construction firm — public site, a ten-step range-based build-cost estimator with confidence bands and server-side PDF export, and a client portal for milestones, client decisions and change control with a running approved-cost total. Confirmed-facts-only content governance: unverified claims stay unpublished by rule.

Next.js 15 · TypeScriptPrisma · PostgreSQLClient portalPrivacy-by-design
New tab Client build · design & estimator preview with demo data
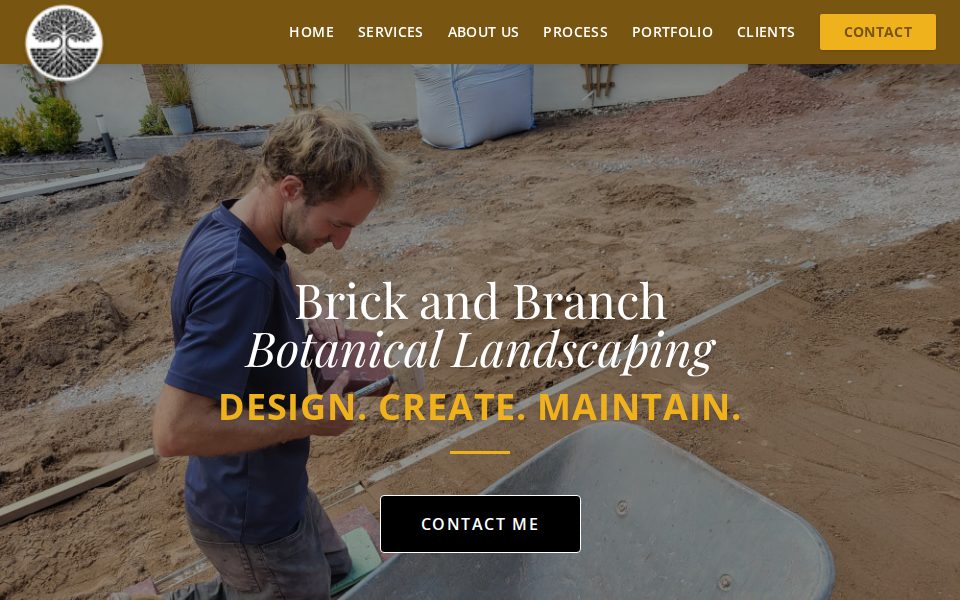
Commercial client build▶ Preview Brick & Branch Botanical Landscaping — home page

Brick & Branch Botanical Landscaping Website · designed and built

The public site for a Worcestershire garden-design, landscaping and maintenance business — services, a three-step process, a filterable project portfolio, client testimonials and an enquiry form. Designed and built by me end to end, for a client whose own work is in soil and stone rather than software.

Hand-built static site · TailwindPortfolio & enquiriesKempsey & Worcester
Visit the site Live client site · design, build and copy
Professional experience

Board-level leadership, hands-on delivery

Legal, Compliance & Technology Consultant

Keystone Analytics — multinational app / data / AI (US parent & Philippine fintech arm)
2022 – Present · advisory (project-based)
  • Advise on legal, compliance, financial and strategic matters while shaping data and risk logic, compliance frameworks and governance — contributing proprietary tooling and IP, including scraping and analyst tooling carried over from my Victory Finance quantitative work.
  • Design and oversee agentic-LLM workflows with human-in-the-loop over REST/JSON and webhooks; hands-on exposure to OneTrust, ServiceNow GRC, TrustArc and NAVEX — under controls aligned to the group’s governing regimes (US federal & Texas money-services; Philippine BSP, AMLA and Data Privacy Act), with FINMA-aligned controls (readiness) and EU DORA awareness.
  • Supported a $2M+ solar initiative (public–private JV) — authored the white paper and investor deck and restructured the financing — and shaped the compliance and rollout framework for AidNow, a verified emergency-services directory app (Philippines).
  • Conceived DipRadar — a personal-research equity screener that scans the S&P 500 for discounts to analyst price targets and ranks the candidates by a composite signal score, with watchlists and diff-based alerts. I brought the concept, market intelligence and initial IP (from my Victory Finance quantitative work); it was built and delivered by Keystone Analytics, and we share the IP in the delivered app. It ships an explicit “not financial advice” disclaimer, with signal definitions credited to publicly available Pristine Capital / Andrew O’Connell educational material.

Director · Head of Legal, Compliance & Operations

Red Spark Learning C.I.C. — eight-site UK adult-education social enterprise
2015 – Aug 2024 · Statutory director from Jul 2021, through wind-down (dissolved 2025)
  • Central to the organisation from 2015; formally appointed Director in July 2021. Owned legal, compliance and operations at board level across eight sites — the largest independent adult-learning provider across the three counties it served, outside the colleges and universities. Built and led the team through a compliant restructuring to a 100% audit pass, with no adverse findings.
  • Ran early-stage dispute resolution and settlement strategy on vendor and employment matters — resolving them before tribunal or formal proceedings.
  • Ran contract lifecycle management end-to-end through CLM and e-signature systems, and delivered the full GDPR programme (DPIAs, DSARs, RoPA, retention).
  • Built Python regulatory-monitoring pipelines that flag policy changes and trigger tasks, approvals and records — feeding risk registers, dashboards and board-level reporting with cross-site trend analysis.
  • Delivered a paper-to-cloud implementation in under three months (−30% operating cost, full continuity); secured £200,000 ESF / Lottery funding and authored £500k+ in competitive bids.

Founder & Technical Lead

Victory Finance Ltd. — proprietary fintech venture
Oct 2023 – Feb 2026
  • Built a Python quantitative trading and risk stack around a policy-to-market signal: legislative, regulatory and geopolitical feeds consolidated into one pipeline (Pandas, REST/JSON APIs) with event-driven logic that measured how comparable policy developments had historically moved prices, weighed alongside company fundamentals and the conventionally analysed factors. The same regulatory-monitoring discipline as the pipelines I built at Red Spark — with a market price attached as the test of whether the signal was real. Board-level risk reporting throughout; a personal proprietary vehicle, closed in an orderly, compliant wind-down.
  • Over the life of the strategy (Feb 2021 – Dec 2025): ≈25% a year, time-weighted, at a 69% win rate and a profit factor of 2.2 across 222 self-directed closed positions. Full broker statement available on request. Personal capital; not financial advice.

Board Member / Trustee

HVOSS (Herefordshire Voluntary Organisations Support Service) — VCSE-support charity
Oct 2022 – Jul 2024
  • Independent non-executive governance, legal and financial oversight for a charitable company supporting the county's voluntary and community sector — restricted-funds stewardship, cashflow-first resilience decisions and defensible governance through a period of funding volatility — including redundancy and employment matters where early, evidence-led settlement mitigated £70k+ in potential exposure. My one external board seat, held alongside the executive roles above.
War Room — governance, finance & crisis operations

The playbook I work from

Nobody Else Is Coming — an operator's playbook for crisis, compliance and capital in organisations too small to have a department for it. First edition, October 2026 (doi:10.5281/zenodo.23462160): a method in nine chapters, three domains with the law stated as at October 2026, and a worked case at the end of each. The three cases are set out below as six-page case studies, each with a link to the chapter it comes from.

Illustrations, not records. The playbook's worked cases are built on invented organisations and figures to show the method in use — a wrong turn, a dilemma the method did not settle, and what it cost. They are not redacted real matters, and no former employer's, client's or funder's information appears in them.

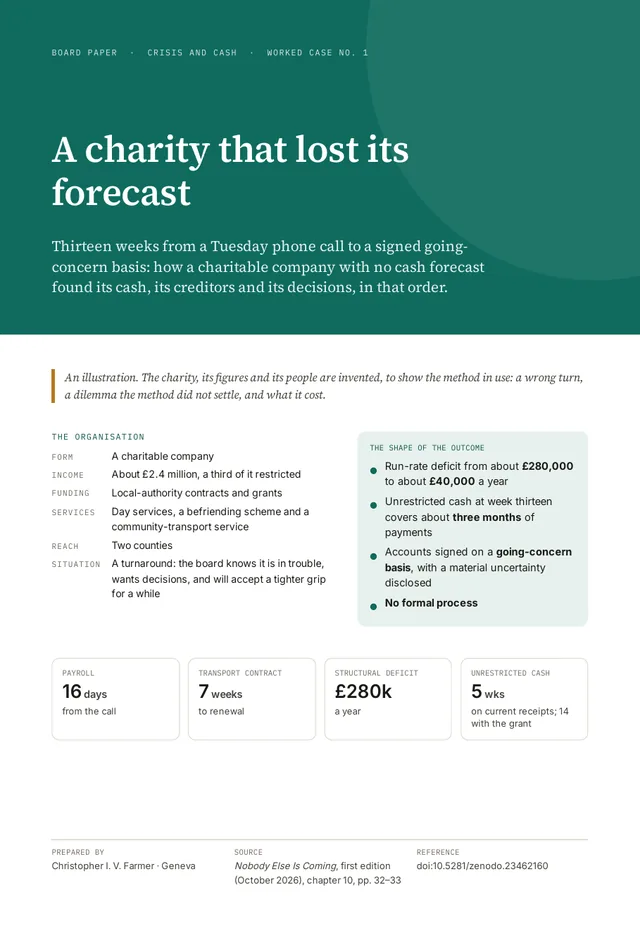
Chapter 10 · crisis and cash · case study, 6 pages

A charity that lost its forecast

A charitable company with no cash forecast, a resigning finance manager and payroll in sixteen days. Thirteen weeks to a signed going-concern basis: the thirteen-week forecast, creditors by class, an options appraisal with a blank pensions line, and the dilemma the method did not settle.

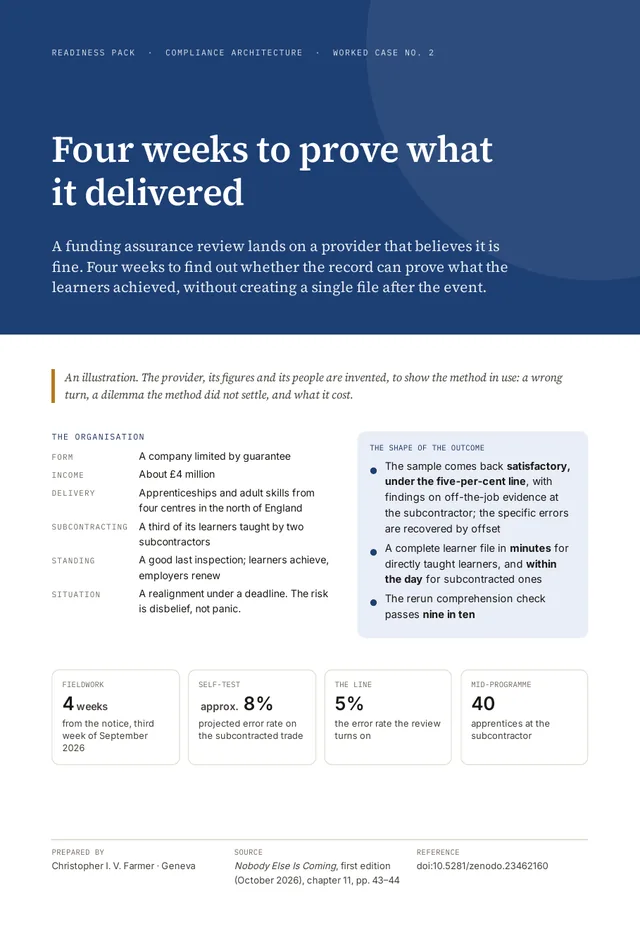
Chapter 11 · compliance architecture · case study, 6 pages

Four weeks to prove what it delivered

A training provider given four weeks’ notice of a funding assurance review, with a third of its learners taught by subcontractors and no one owning their evidence. The self-test, the written instruction that nothing is created after the event, a chatbot in the progress reviews, and an attestation rate that measured clicking.

Chapter 12 · capital and structure · case study, 6 pages

A founder who nearly sold the plant to build it

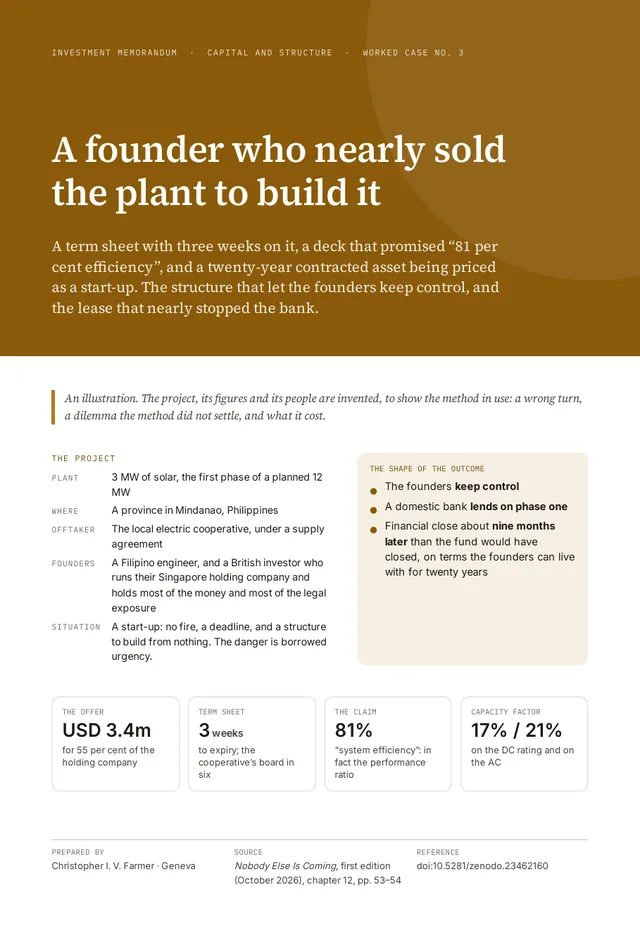
A 3 MW solar project in Mindanao, a venture fund offering USD 3.4 million for 55 per cent, and a deck promising “81 per cent efficiency”. Venture or asset; the three numbers behind the claim; the structure that let the founders keep control; the ninety-nine-year lease that nearly stopped the bank.

Example deliverables

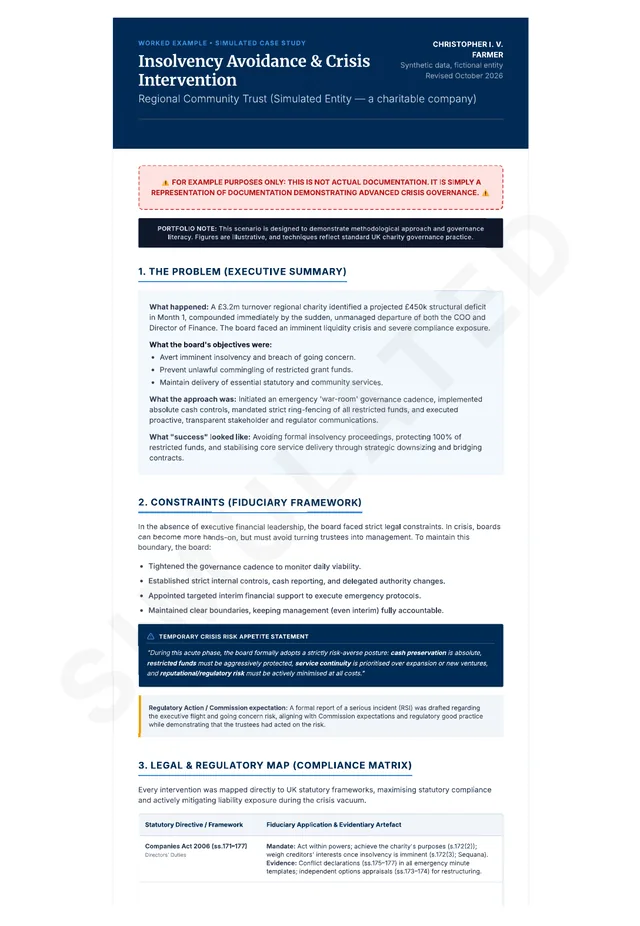
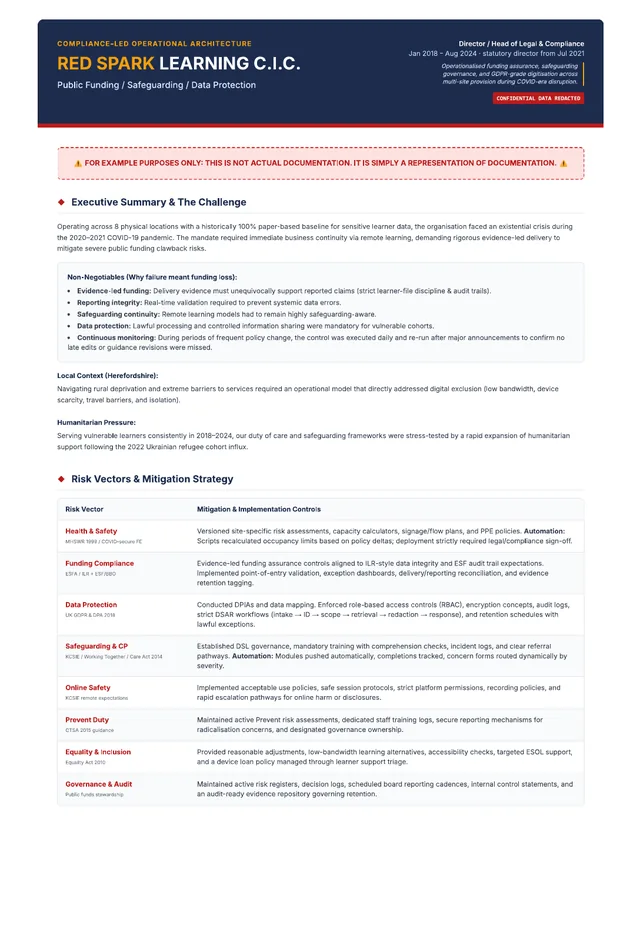
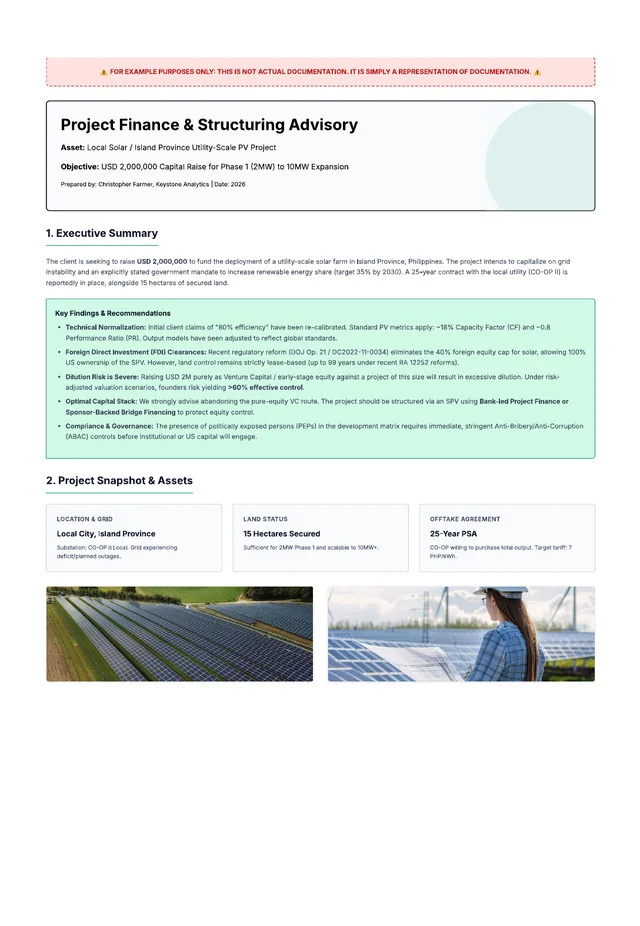
Three documents of the kind the method produces, kept apart from the playbook’s invented cases: a simulated crisis plan, the controls I ran at Red Spark Learning with confidential details redacted, and a project-finance advisory with client and place names removed. Each PDF is an image of the page; the card carries its text.

Simulated worked example · 7 pages

Insolvency Avoidance and Crisis Intervention

A crisis-intervention plan for a charity facing a £450k structural deficit after two senior executives left suddenly: the trustees’ duties, emergency governance and controls, a thirteen-week cash plan and the board’s options appraisal. The organisation and every figure in it are invented.

Real controls, redacted · 4 pages

Red Spark Learning C.I.C. — Operational Scaling

A representation of the documentation of the compliance and operating controls I ran as Director and Head of Legal & Compliance at Red Spark Learning C.I.C., 2018–2024 (statutory director from July 2021): eight sites moved to remote learning, funding assurance, safeguarding and data protection. Not simulated: the figures are real, and confidential details are redacted.

Worked example, names removed · 5 pages

Project Finance and Structuring Advisory

A project-finance and structuring worked example for a utility-scale solar project in a Philippine island province: the technical claims normalised, the foreign-ownership and land-lease rules, the project vehicle and contract stack, and financing routes other than venture capital. Client and place names are removed.

Core competencies & stack

Where the law meets the build

Legal, compliance & operations

Legal, compliance & operations leadership
Contract lifecycle management (CLM) & e-signature
Board & stakeholder management
Funder & regulator engagement
Data privacy & GDPR (DPIA / LIA, DSARs)
Risk, GRC & audit
Legal intake & triage
Requirements & solution design

Legal, GRC & policy tooling

Legal draftingLexisNexis · WestlawDocuSign CLMiManage / NetDocumentsRisk registersPolicy architecture

Compliance platforms — familiarity / exposure

World-CheckChainalysisOneTrustTrustArcNAVEXServiceNow GRC

Hands-on build — automation-focused, not production dev

Build & scripting

Python (pandas, matplotlib, regex)SQLREST/JSON APIs · webhooksVBAMS Access / Excel automationHTML · CSS · JSMQL5 · thinkScript

AI & automation

Agentic-LLM workflows (HITL)GenAI control mapping

Data, BI & delivery

Power BIExcel (advanced)Jira · ConfluenceMicrosoft 365Adobe Photoshop

Domain & controls

FINMA-aligned controls (readiness)EU DORA awarenessEU AI Act (provider/deployer roles)UK Data (Use and Access) Act 2025Swiss FADP / nFADP (awareness)Swiss AMLA / Transparency Register (readiness — in force 1 Oct 2026)DPIA / LIARegulatory-obligation tracking

Additional familiarity (read / edit / adapt, not production development): R, Java, C#.

Implementation ownership

Confident to own an intake build and CLM rollout end-to-end — templates, intake logic, approval workflows and permissions, playbooks, fallback language and clause libraries — with self-service contracting, legal-review gates and full post-signature auditability, wired over REST/JSON and webhooks into executive dashboards for matter volumes, SLA performance, privacy-risk trends and compliance readiness. I have scoped exactly this kind of rollout: a Streamline intake build and a Juro CLM rollout, with Catylex clause enrichment across ServiceNow, OneTrust and Close. Governing it was a multi-jurisdiction privacy matrix — EU, UK, US, Australia and New Zealand, with EU AI Act role analysis — that maps every data flow to its controlling regime before a record moves. The same regime-by-regime structure extends to the Swiss FADP (nFADP), with its Swiss-specific divergences, for a Geneva deployment.

Confidentiality, AI & jurisdictions

All portfolio data here is synthetic or public. In client work I operate on least privilege, keep privileged material out of third-party models unless contractually cleared, and gate every automated workflow behind human review — legal professional privilege and data-protection duties sit above delivery speed.

Jurisdictions worked across: England & Wales (5+ years SRA-qualifying work experience; formal submission pending, SQE planned) · Switzerland · EU

For the record: not a litigator, and not a production software engineer — a legal & operations leader who builds working tools to a professional standard, and knows exactly where that line sits.

Education, qualifications & writing

Credentials

Education

2022 – 2024
LL.M. Legal Practice — International Law
University of Worcester. Dissertation: “Economic Warfare: The Unregulated War” (doi:10.5281/zenodo.23462116) — awarded 100%. It proposes a legislative framework (UK-EWPRA) against cyber-economic aggression, market manipulation and proxy financial tactics, and led to an invitation to pursue doctoral research.
2016 – 2020
B.A. (Hons) Politics, Philosophy & Economics — Economics major (2:1)
Goldsmiths, University of London. Focus areas: Macroeconomics, International Economics, Banking, Political Theory, African Conflict & Peacekeeping, Game Theory. Model UN & debate; university radio commentator on macro-policy.

Qualification & membership

Solicitor route
Solicitor route (England & Wales). More than five years of confirmed SRA qualifying work experience; formal submission pending. SQE planned — not admitted. ~6 years in legal & compliance.
Member
International Law Association
In progress
French — B1, working towards B2; CAMS to follow — formalising AML and sanctions capability for Swiss / European roles.
Languages
English (native) · French (B1, working towards B2) · Spanish (basic)

Research

My research sits where international law, economic security and computational method meet. My LL.M. dissertation, “Economic Warfare: The Unregulated War” (awarded 100%), argues that economic warfare — cyber-economic aggression, financial terrorism and the strategic manipulation of markets — has become a favoured mode of conflict for state and non-state actors alike, increasingly waged through third-party proxies that evade legal accountability. It shows why instruments such as the Sanctions and Anti-Money Laundering Act 2018 and the Magnitsky Act, though significant, are too narrow and too slow, and proposes the UK Economic Warfare Prevention and Response Act (UK-EWPRA): a deliberately adaptable legislative architecture — UK-anchored but globally extensible — designed to keep pace with algorithmic and cyber warfare.

Doctoral direction (in development). Following the dissertation I was invited to pursue doctoral research (economic & cyber warfare), and am developing my own project on the regulation of AI — building on my work on AI as an autonomous third-party actor — written in Geneva alongside professional work. It is the next step beyond the private military companies and proxies of my dissertation: systems that can act, and cause harm, at arm's length from any accountable principal. My argument is that the answer is not only reinterpreting existing international law, but small, modular internal policies that many states can adopt quickly — in the spirit of the Magnitsky Act — so regulation moves at the speed of the technology it governs.

Research interests

AI accountability & autonomous actorsEconomic & cyber warfare and the lawAdaptive / modular regulationSanctions & proxy-financeLegal-tech & computational complianceAML & privacy governance

Curriculum vitae & references

A single CV, deliberately — the depth sits in the case studies and publications rather than in a longer document. Reference letters below; further references on request.

Get in touch

Contact

Geneva, Switzerland Swiss B permit — work-authorised, no sponsorship needed
+33 6 82 91 37 80Mobile · French number, Geneva-based

Currently

Open to legal, strategy and AI-transformation roles in Geneva — legal operations and regulatory change, enterprise risk, controls and resilience, operating-model design and AI governance — and equally to the specialist lanes this portfolio evidences: RegTech / legal engineering and sanctions / financial crime, where owning both the regulatory outcome and the build is the advantage. On the counsel track, solicitor route (England & Wales) — more than five years of confirmed SRA qualifying work experience; formal submission pending, SQE planned.

Email me Save contact